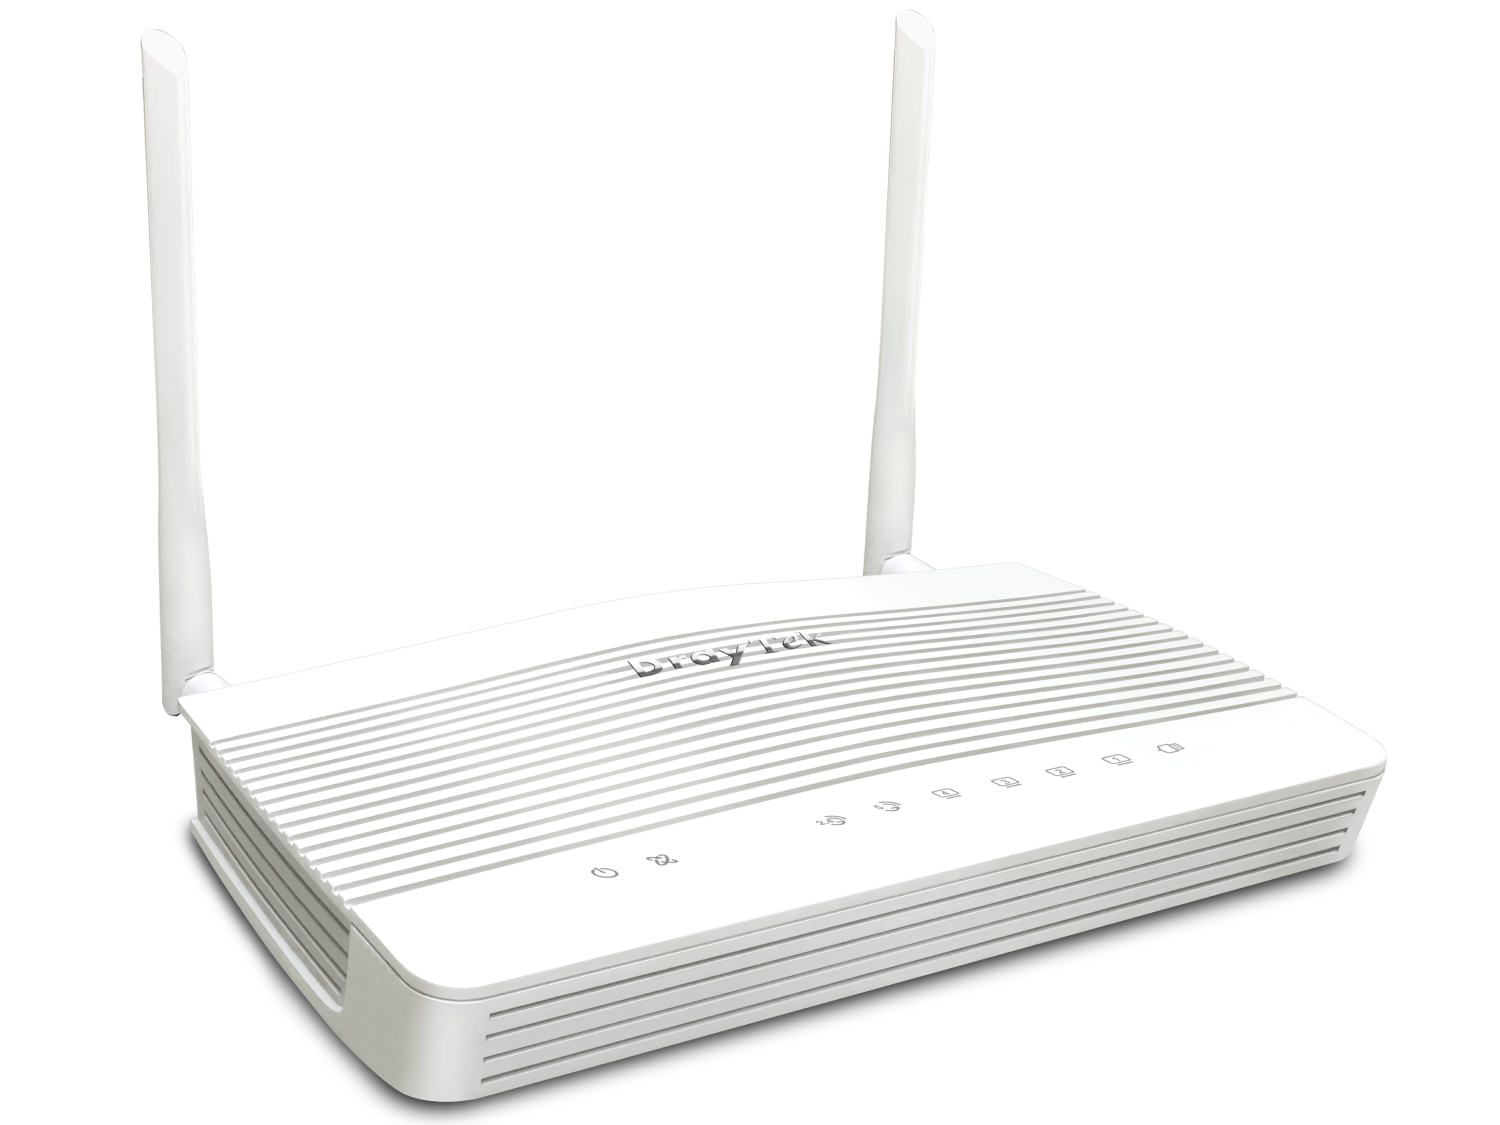
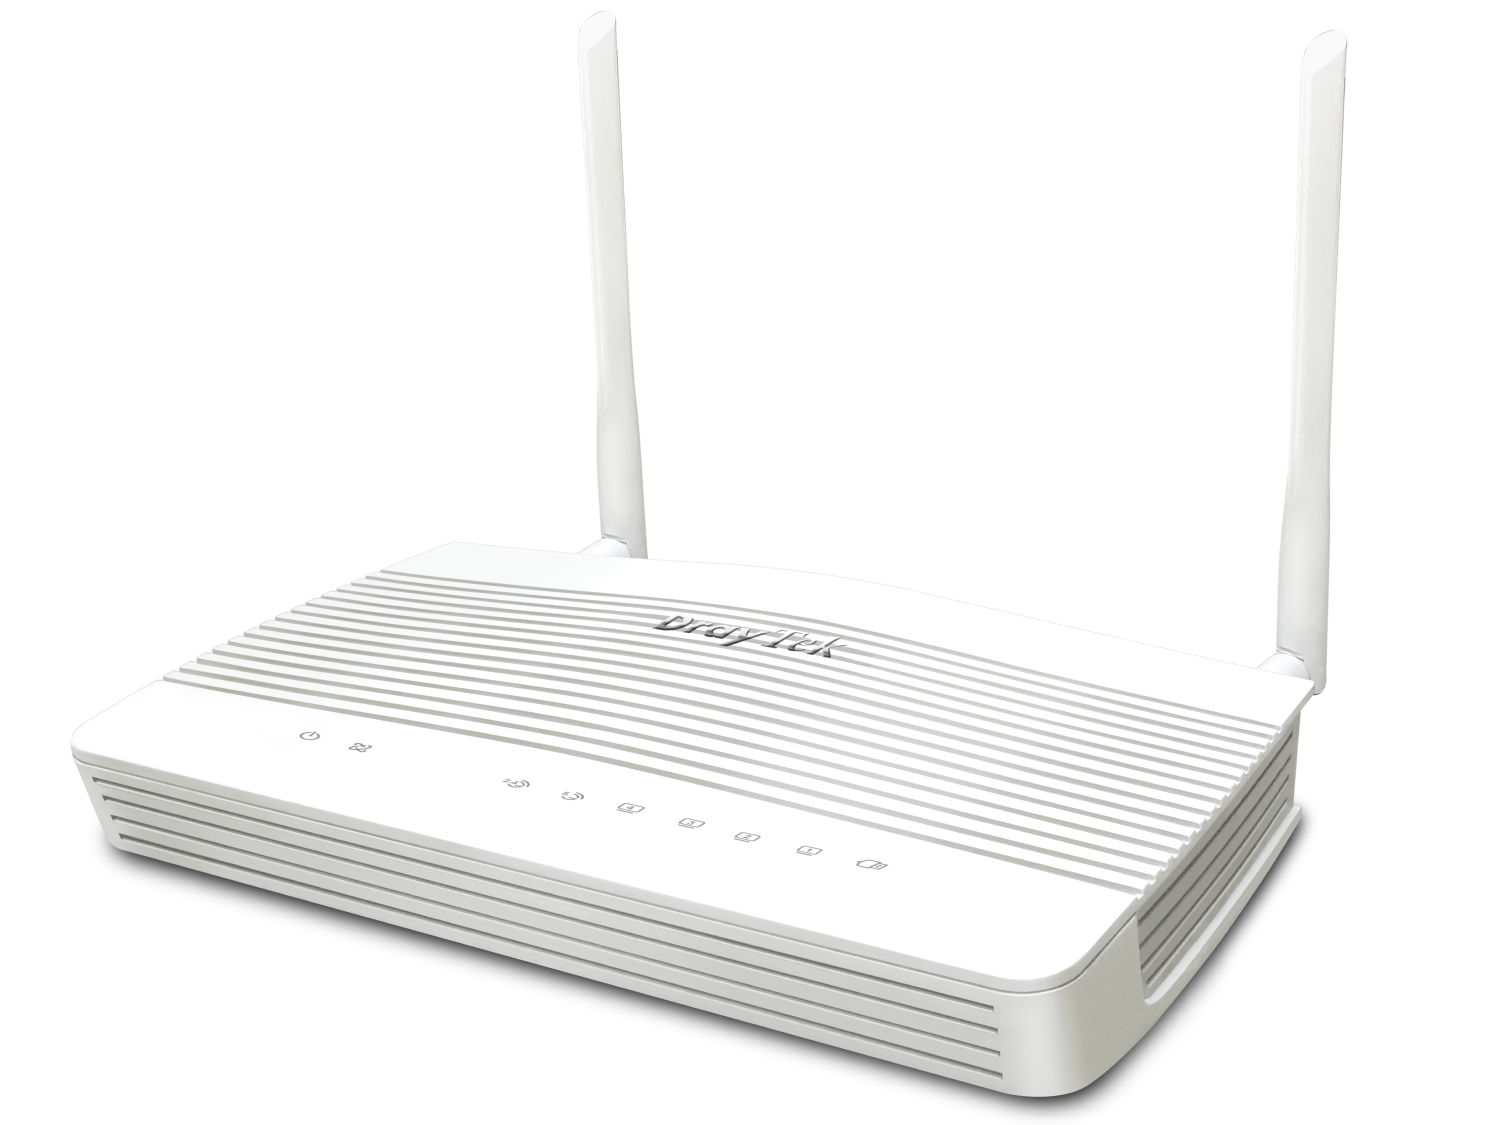
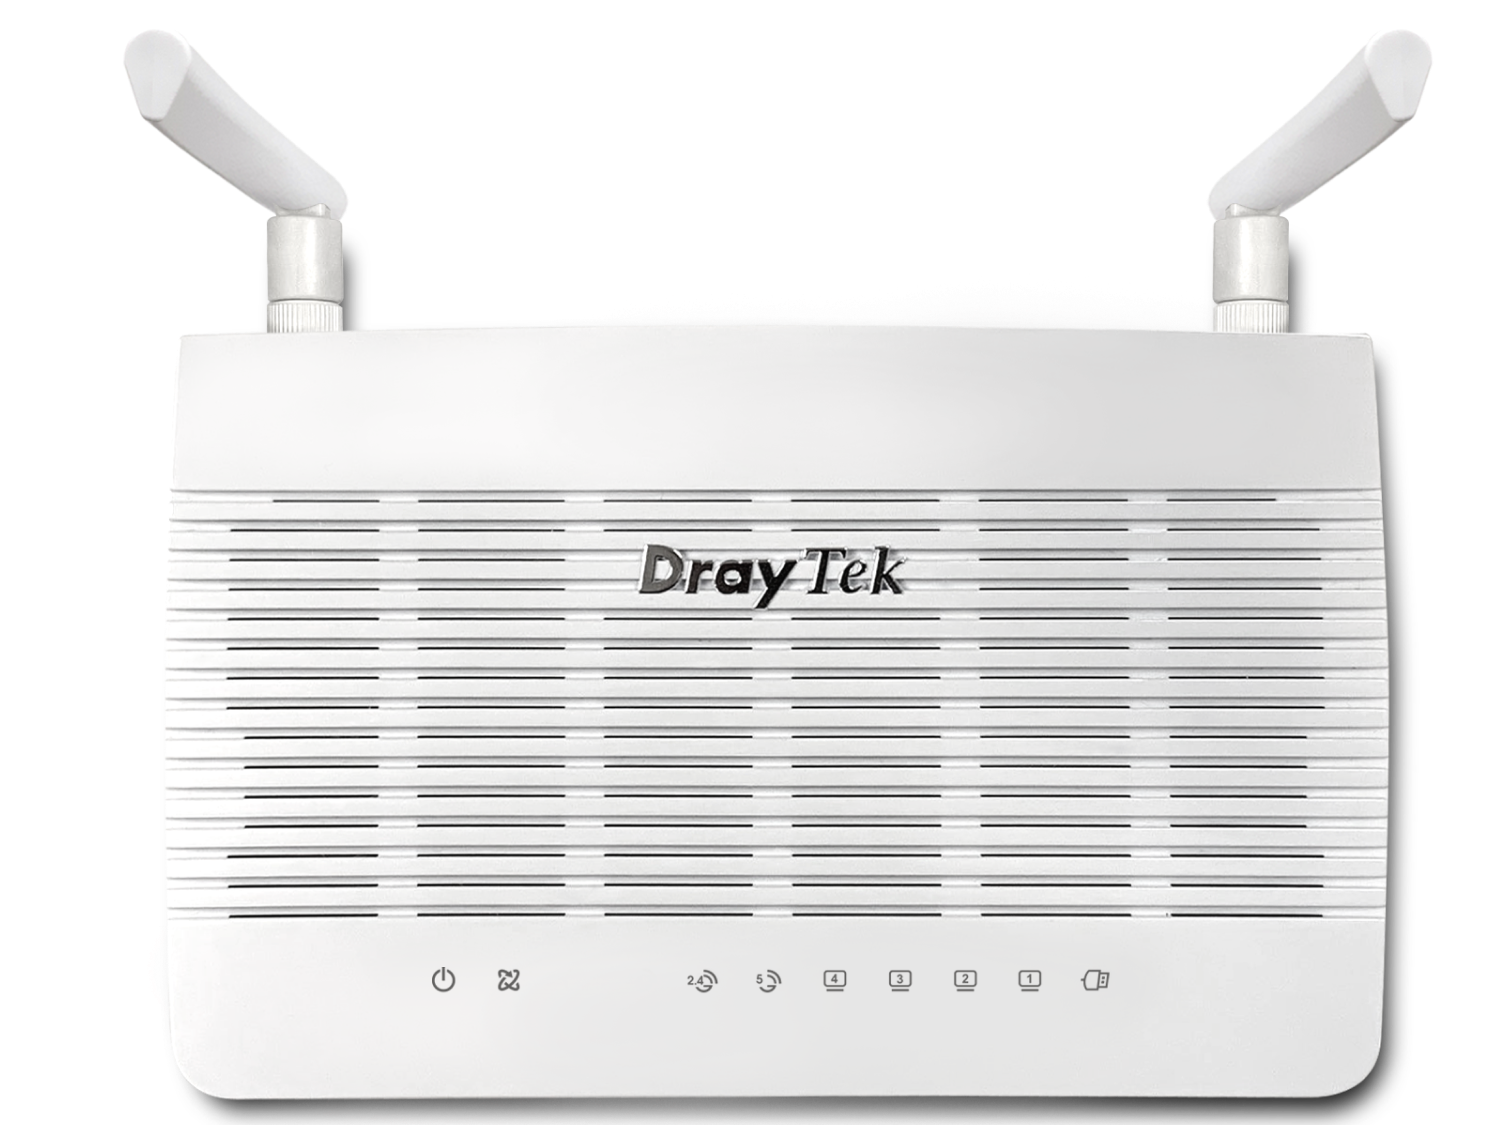
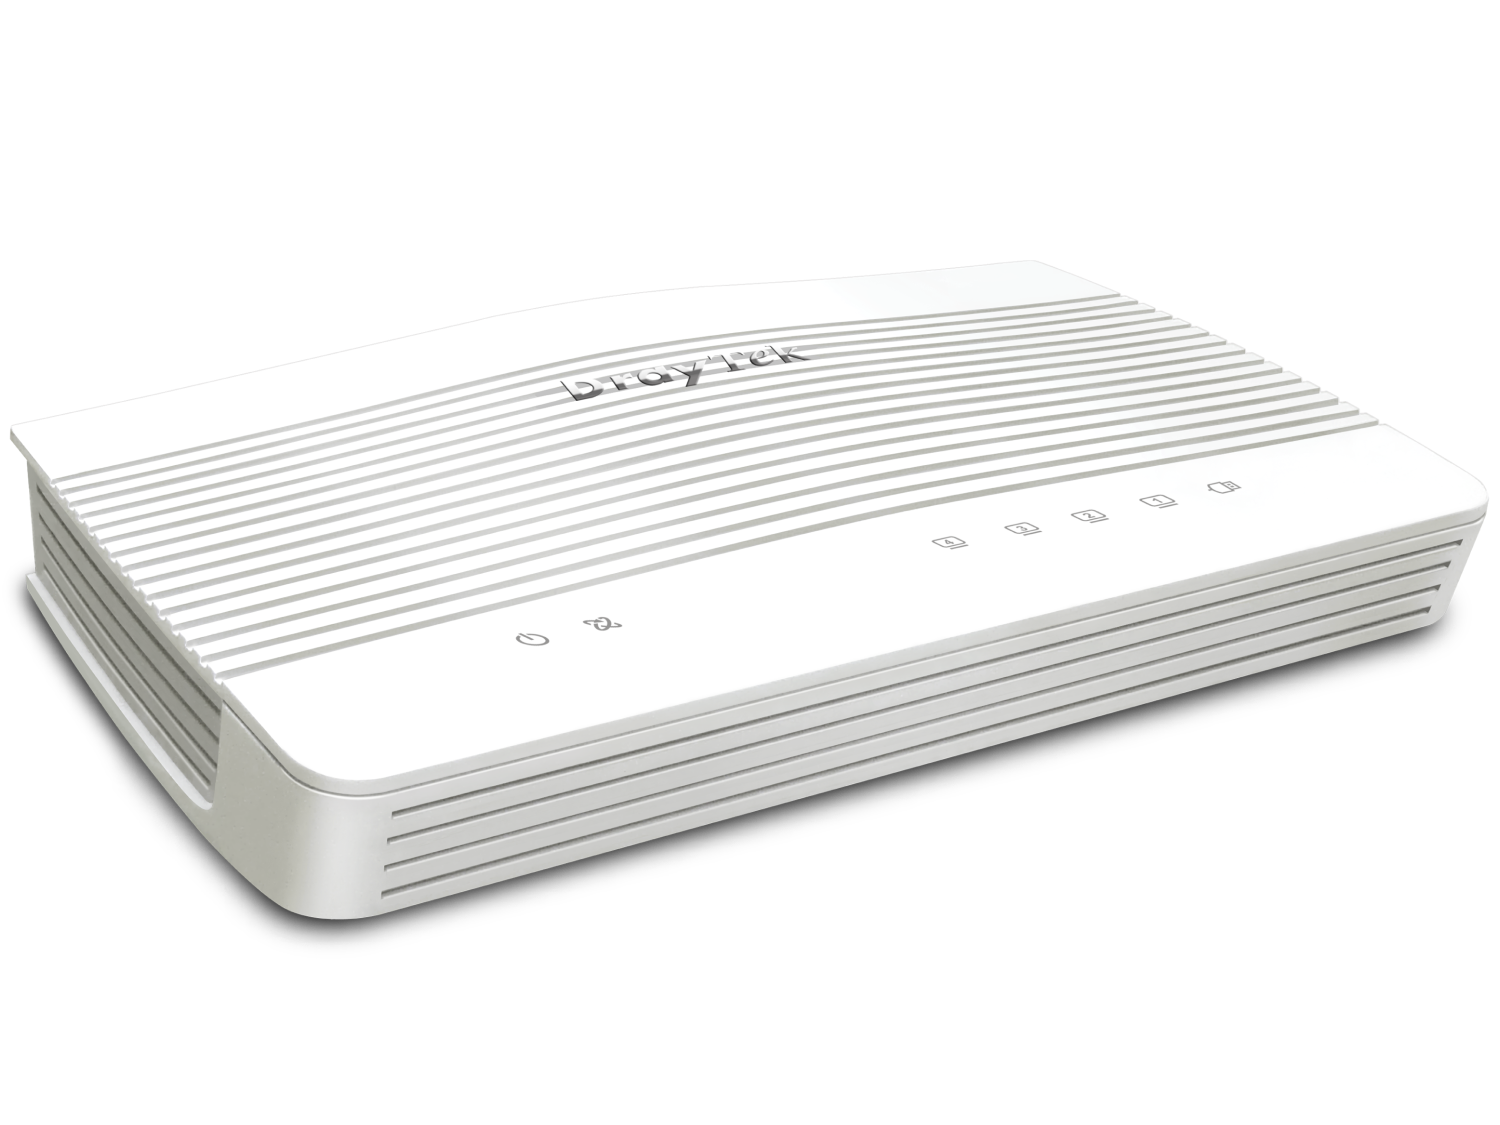
2.5G Dual-WAN Security VPN Router
2.5G WAN Ultra-High Speed Router
Vigor2136 Series is a Dual-WAN broadband VPN router, featuring 2.5G WAN port to deliver fast speed that meets the growing network demands of business. It delivers up to 2.3 Gbps performance without sacrificing bandwidth control features. The router is equipped with business-grade features, including web content filtering, Route Policy, App-based QoS, and more. The series includes models with built-in 802.11ax Wi-Fi.
Overview
Dual-WAN
2.5/1GbE Ethernet
16 VPN
IPsec throughput up to 390 Mbps!
WiFi AX 3000*
Delivers link rate up to 3 Gbps
50k Sessions
Recommended for a network of 30 hosts
*ax model only
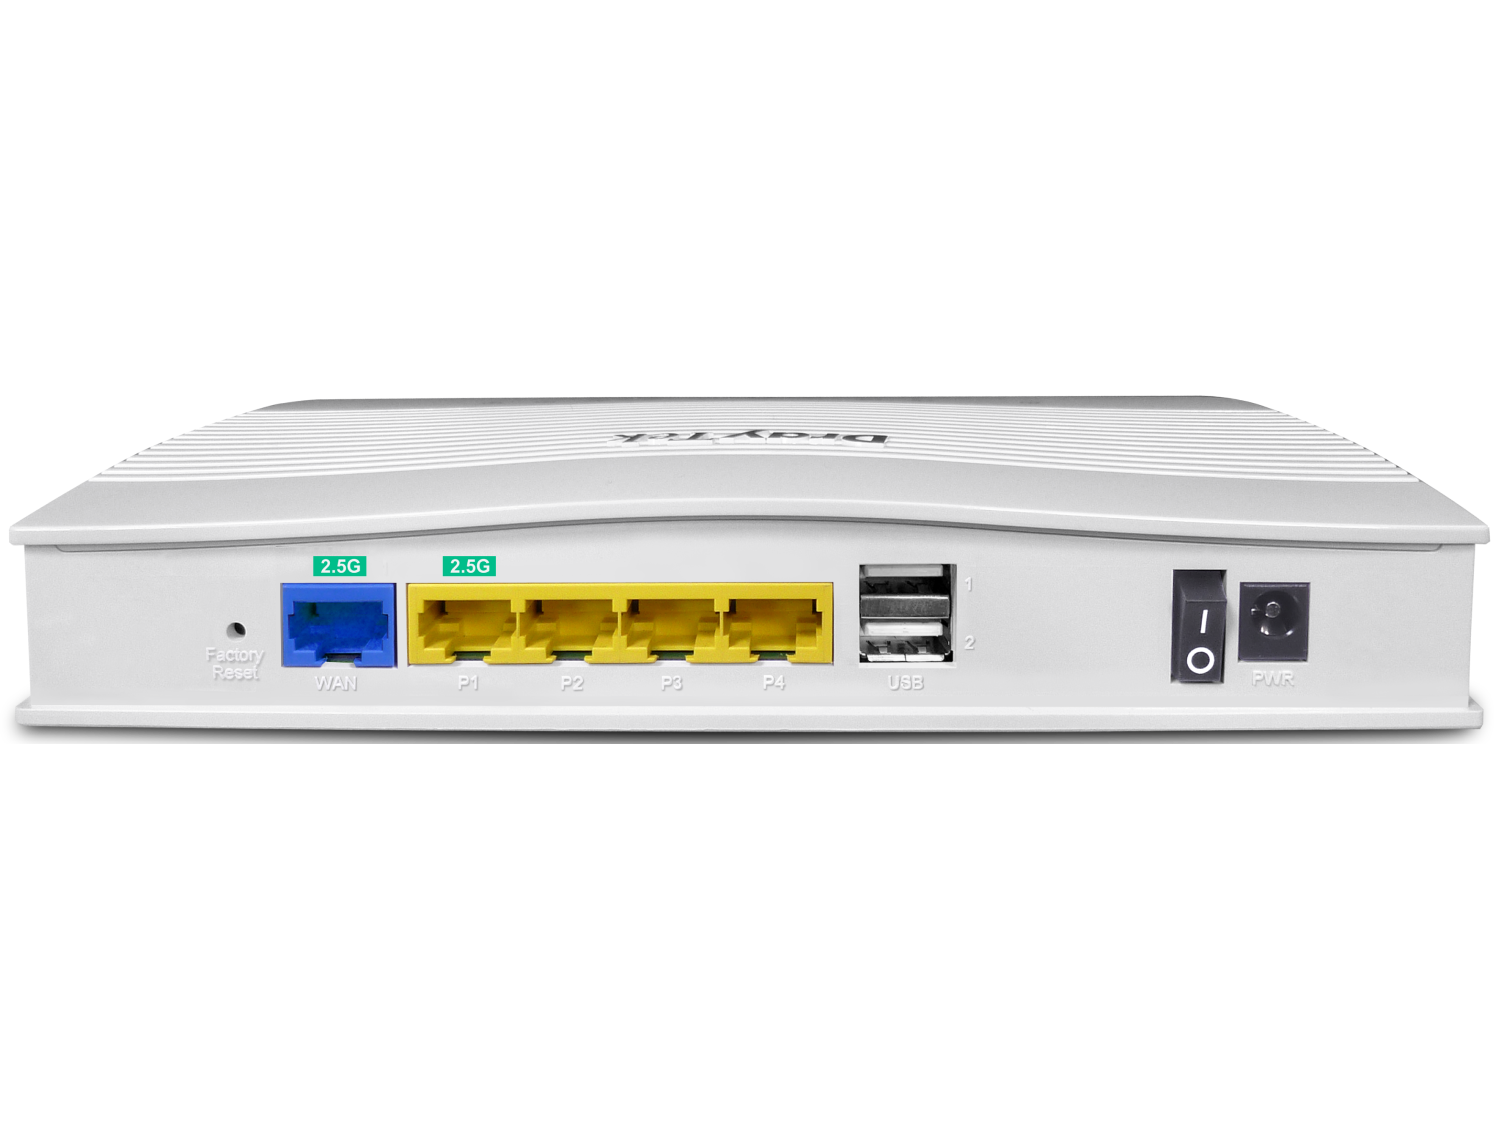
Interface
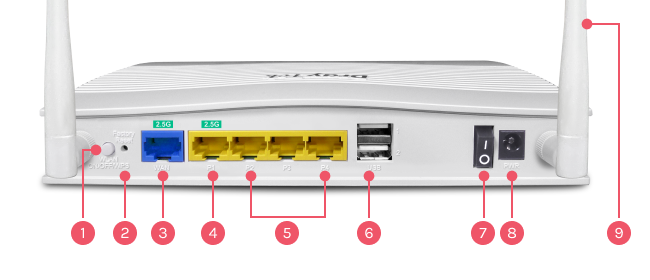
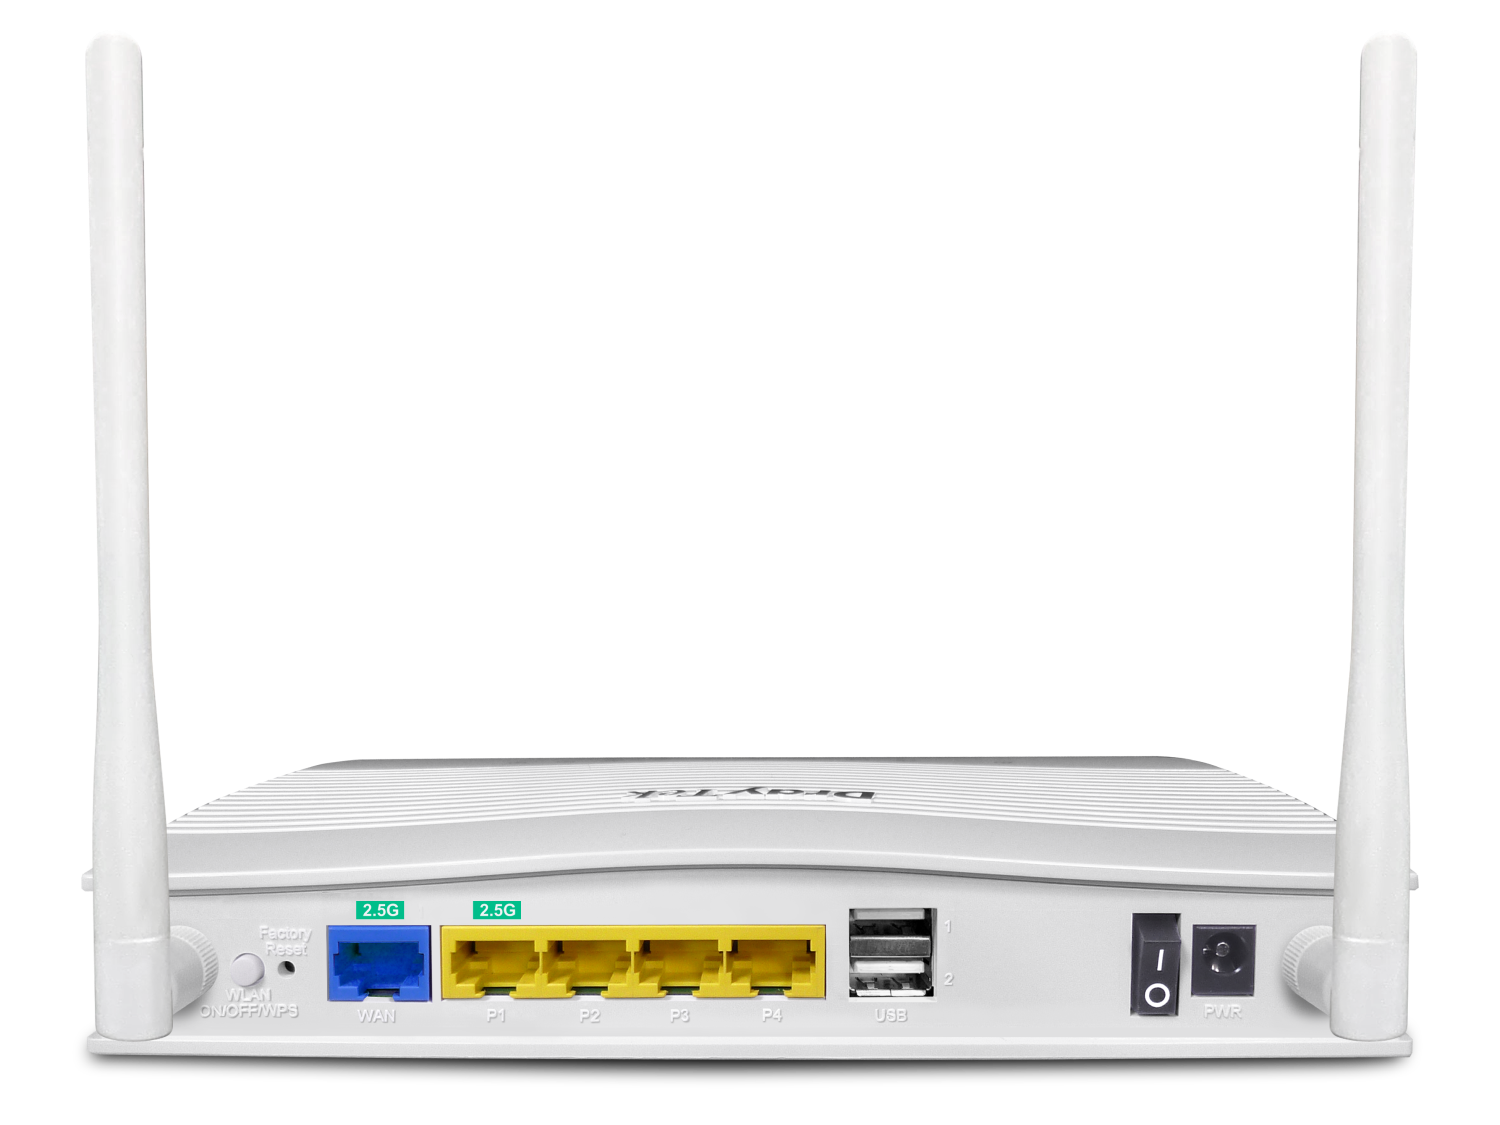
(ax model)
1WLAN/WPS Button (ax model)
2Reset Button
3Fixed WAN Port: 1x 2.5GbE RJ-45
4LAN/WAN Switchable Port: 1x 2.5GbE RJ-45
5Fixed LAN Port: 3x GbE RJ-45
62x USB 2.0
7Power On/Off Switch
8Power Input
9Wi-Fi Antenna (ax model)
Multi-Gig Routers
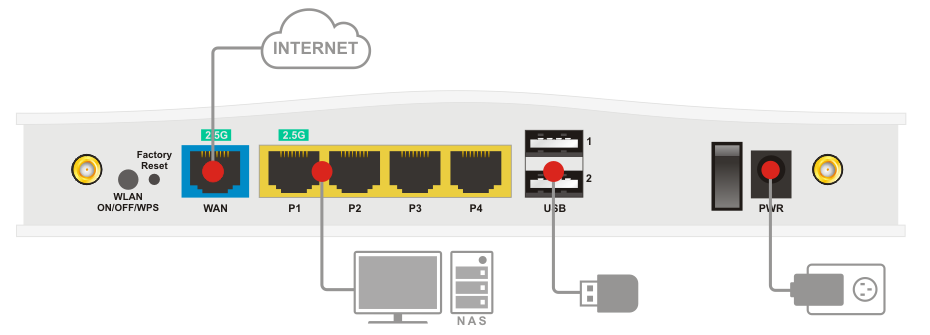
Faster Wired Connections
- 4K video streaming
- online gaming
- large file transfers
- network-attached storage (NAS) devices etc
Beyond Gigabit
Internet speeds of up to 2.5Gbps let users make full use of the available bandwidth.
NAT & Routing Performance
The Vigor2136 Series delivers NAT throughput of up to 2.3Gbps while meeting high QoS expectations. You can easily prioritize business-critical applications and always keep VoIP traffic at top priority.
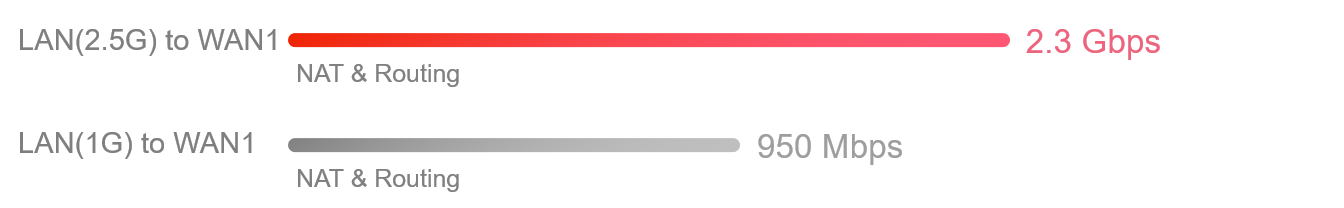
Effortless Secure Access with EasyVPN
Setting up a traditional VPN can be complicated, with protocols to choose and settings to configure by hand. The Vigor2136 Series supports IPsec, WireGuard, and OpenVPN, and EasyVPN simplifies Teleworker VPN: remote users get secure access just by importing a profile.
EasyVPN lets users set up secure connections without the hassle of:
- Generating WireGuard keys
- Importing OpenVPN configuration files
- Uploading certificates
Because EasyVPN automates these steps, every user gets a fast, secure, and easy VPN experience.
Stealth Security Protection with Port Knocking
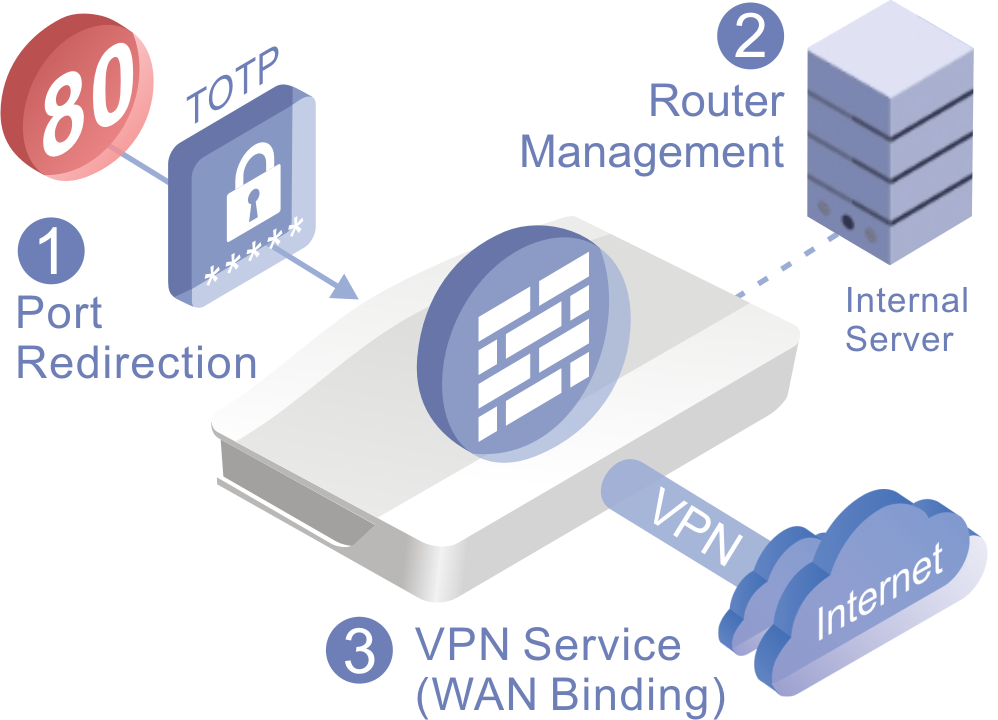
DrayTek’s Port Knocking technology adds an advanced stealth layer of security by hiding critical network services from unauthorized users. Instead of exposing management ports or VPN services to the public internet, Port Knocking requires a predefined “knock” sequence before it grants access, so only trusted users can find and use these services.
Port Knocking combines three key functions to deliver strong protection against port scanning, brute-force attacks, and unauthorized access.
Port Redirection
- Hide your real service ports from the public internet.
- Redirect unauthorized requests to non-existent services, preventing detection.
Router Management Access
- Allow router management only through a secure internal server or after successful knocking.
- Eliminate exposure of the management interface to the open internet.
VPN Service Control (WAN Binding)
- Keep VPN services invisible and inaccessible until the correct knock sequence is received.
- Bind VPN availability to specific WAN interfaces and authorized IP addresses.
How It Works
- In normal state, all targeted ports remain closed and undetectable.
- After the correct knock sequence, selected ports open temporarily for authorized access.
- Once the time window expires, services return to hidden mode automatically.
With DrayTek Port Knocking, your network runs in stealth mode: invisible to attackers, yet instantly available to authorized administrators and remote users. That makes it an ideal solution for organizations that need high security without giving up accessibility.
Vigor2136 2.5G Router with Wi-Fi 6 capacity (ax model)
The Vigor2136 Series is a dual-band Wi-Fi router that uses 160MHz bandwidth and 1024-QAM to greatly increase wireless speed. Its theoretical speed reaches up to 3000Mbps—574Mbps in the 2.4GHz band and 2402Mbps in the 5GHz band—which is 2.5 times faster than an 802.11ac 2×2 dual-band router in the home. It also includes business-grade features such as URL Reputation, Route Policy, App-based QoS, and much more, making it ideal for professional smart-home and SOHO users who want full control of their own network.
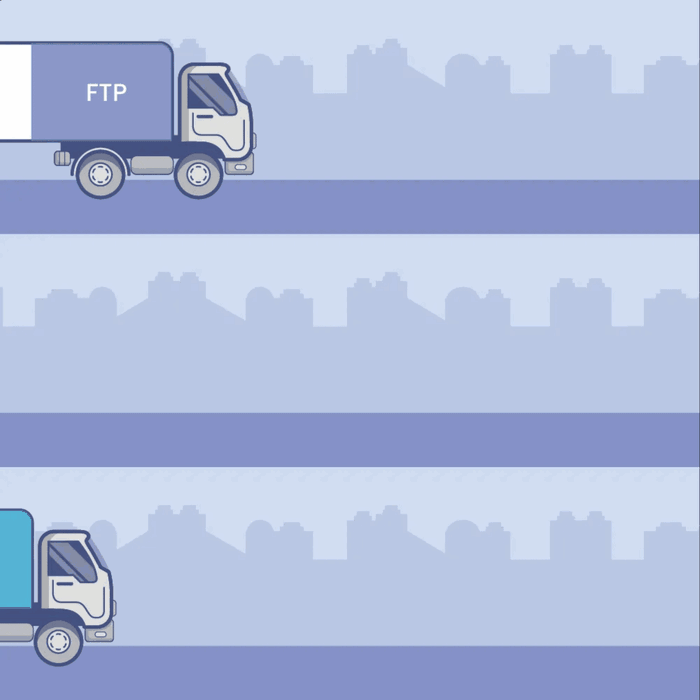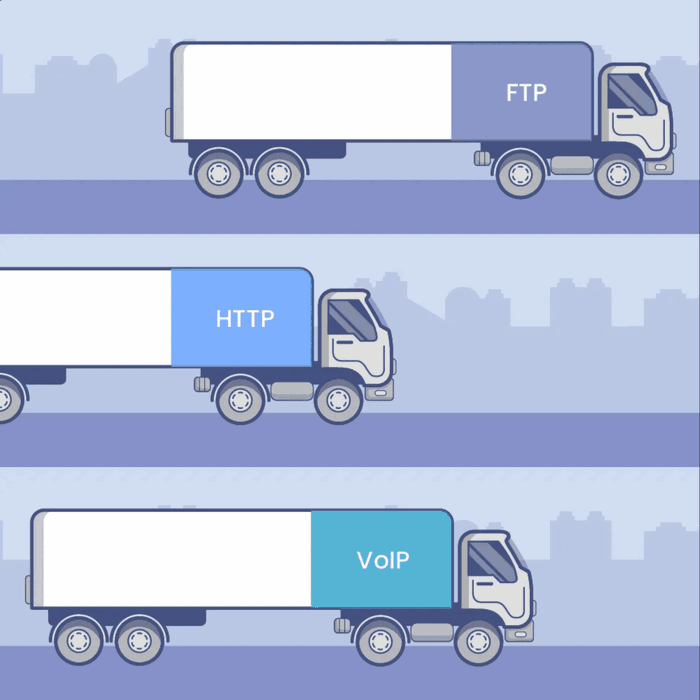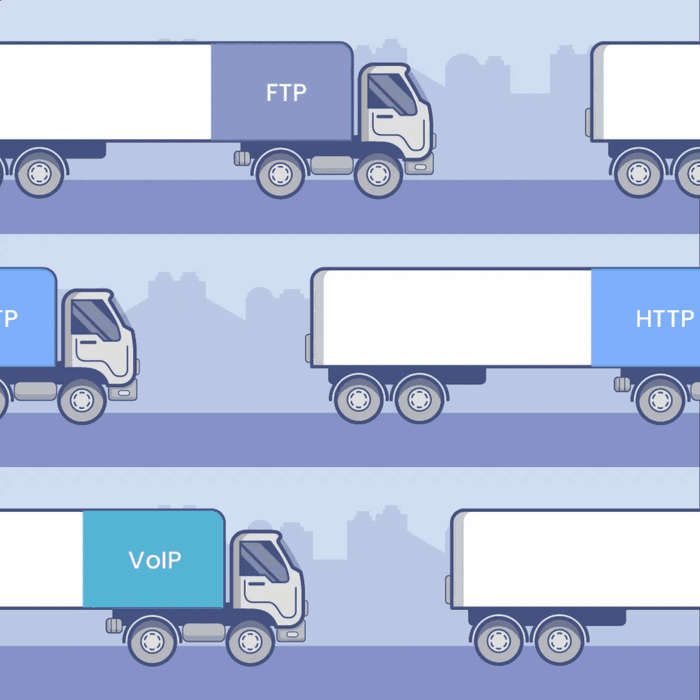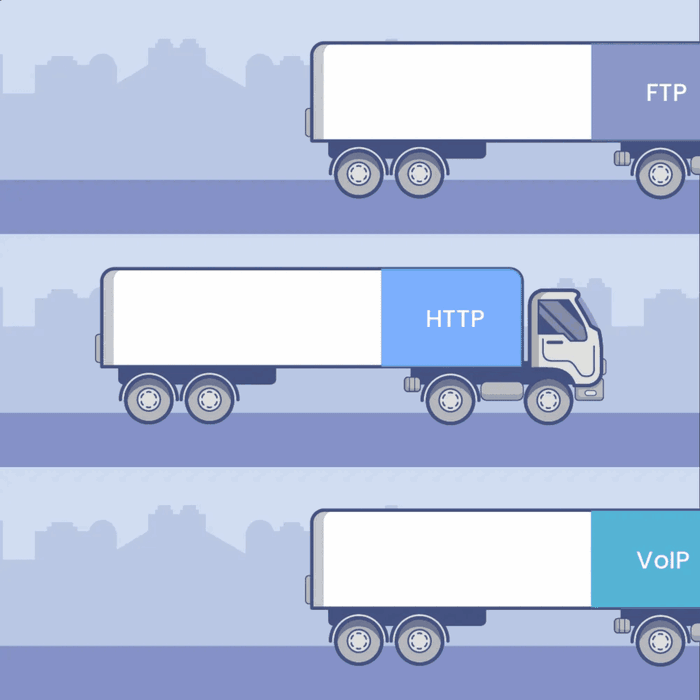
OFDMA (Orthogonal Frequency Division Multiple Access) is a key feature of the Wi-Fi 6 certification program. Part of the Wi-Fi 6 standard, OFDMA relies on efficient scheduling to perform well in congested, complex network environments. As Wi-Fi 6 gains traction among manufacturers and across the industry, it is increasingly important to analyze and document the benefits of a successful OFDMA implementation and to be able to measure its impact.
OFDM
OFDMA
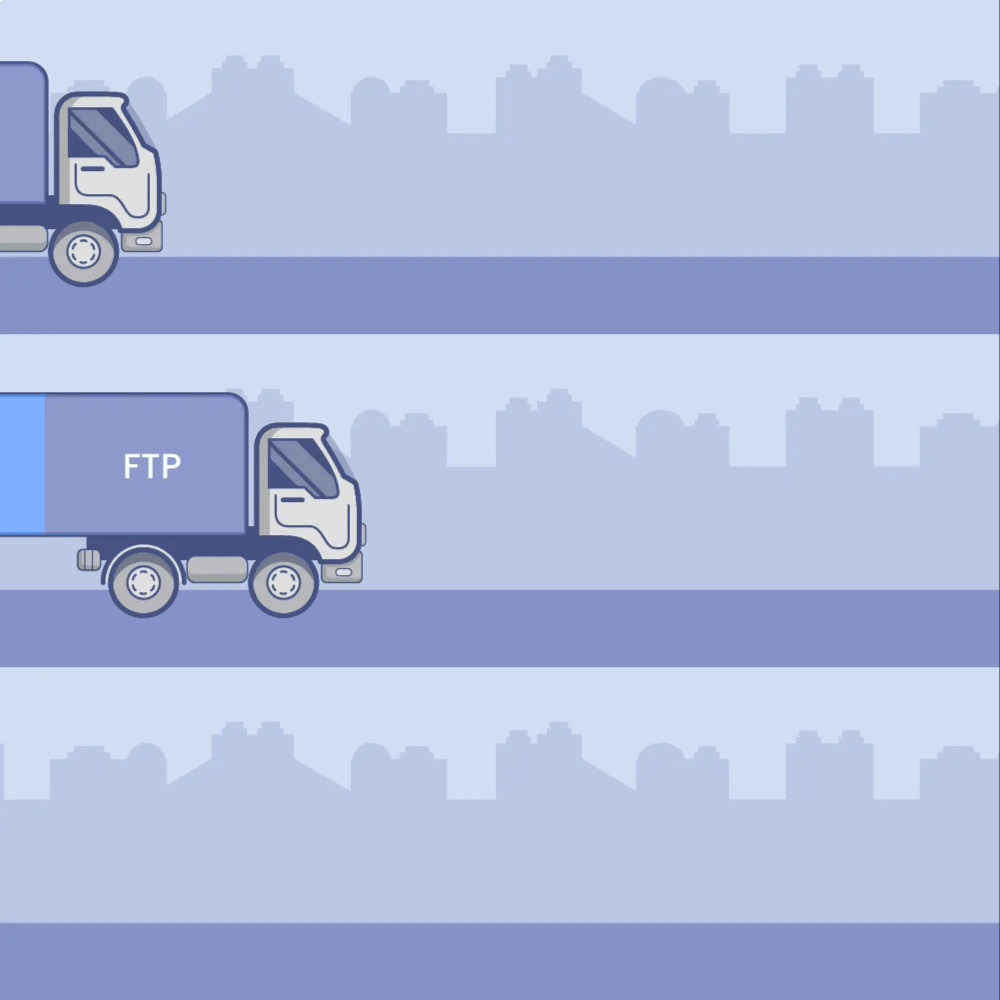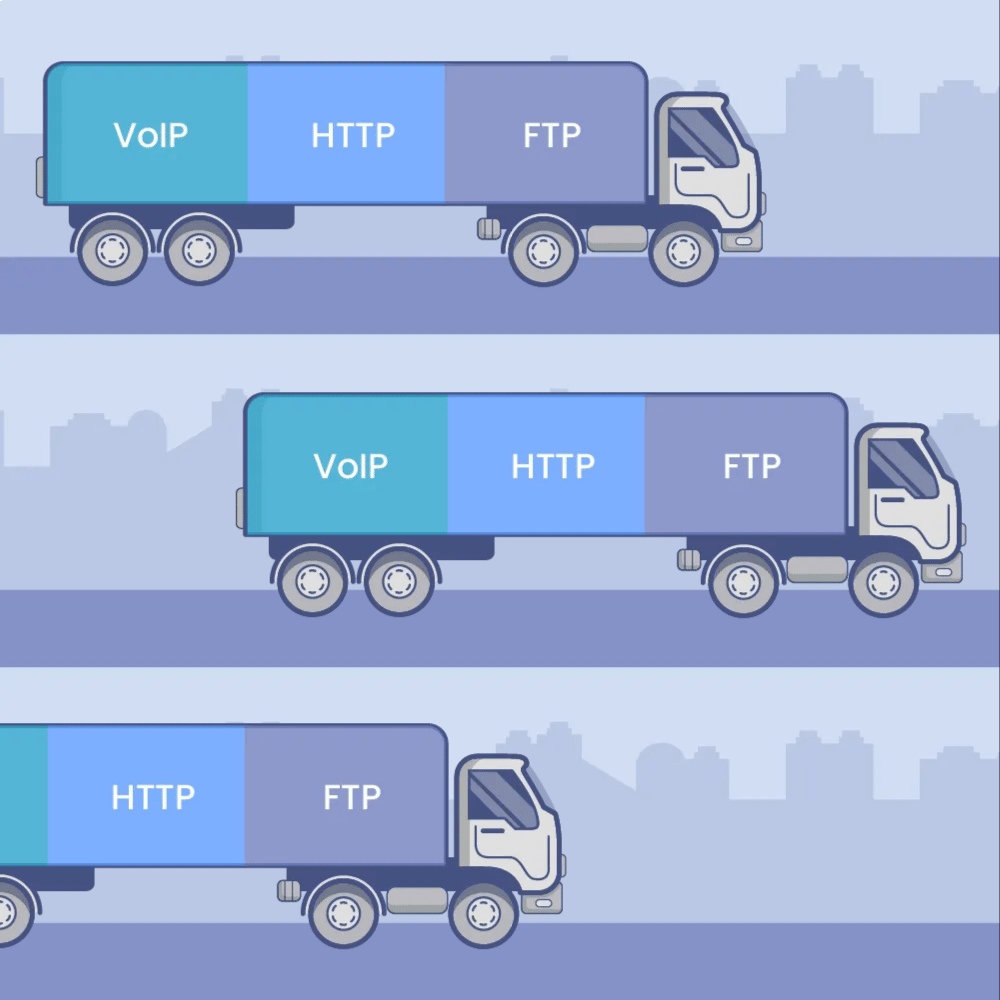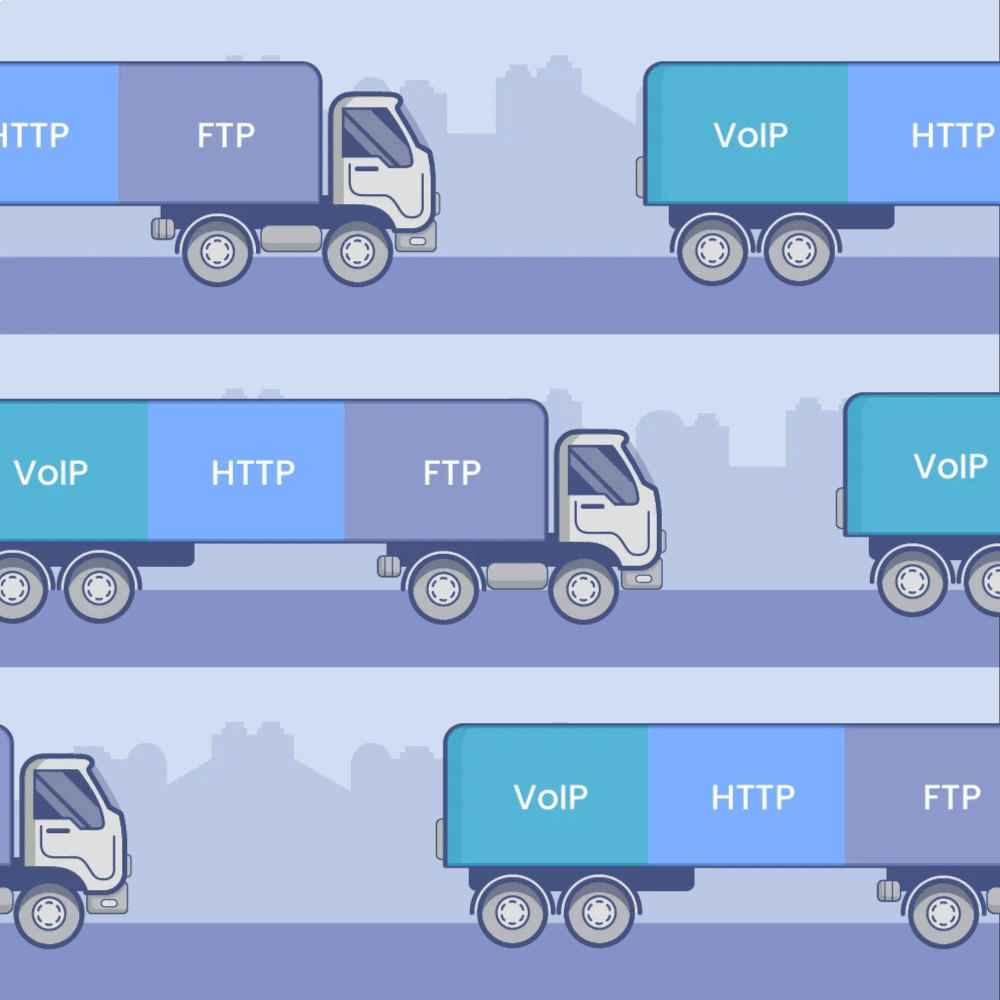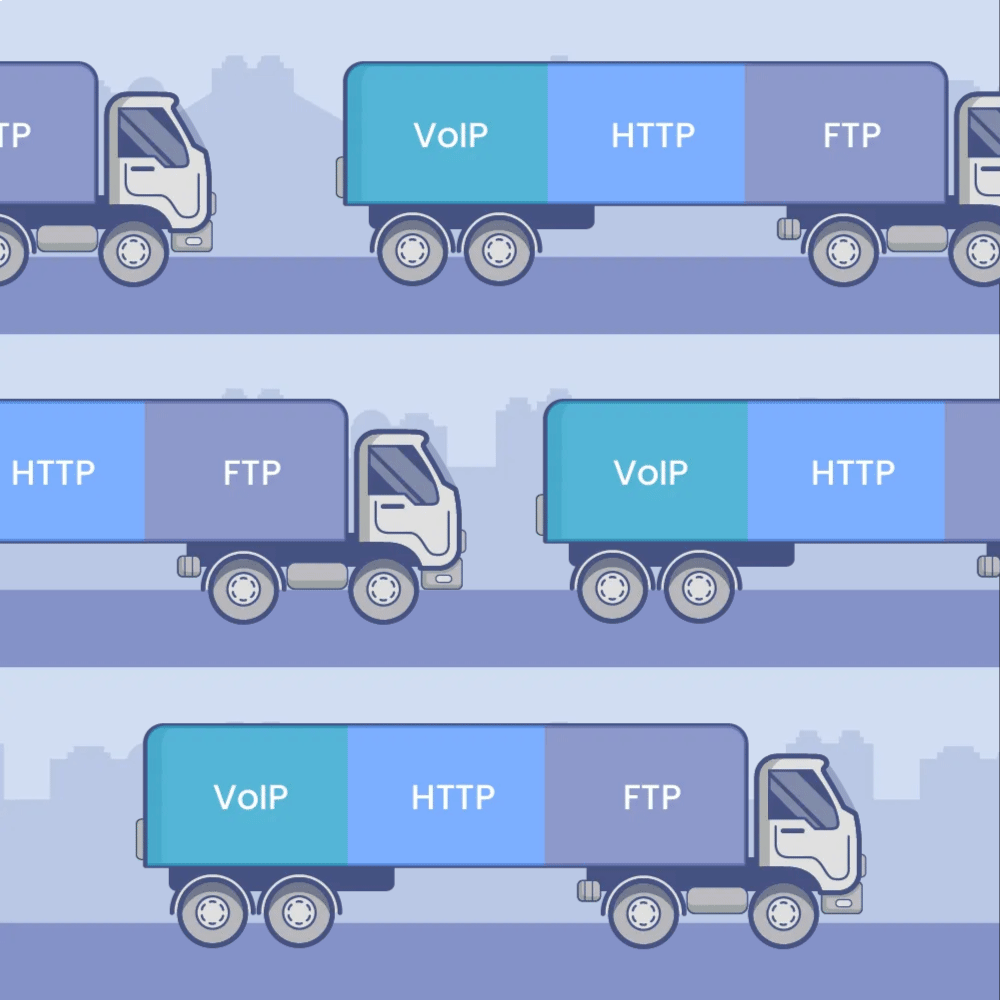
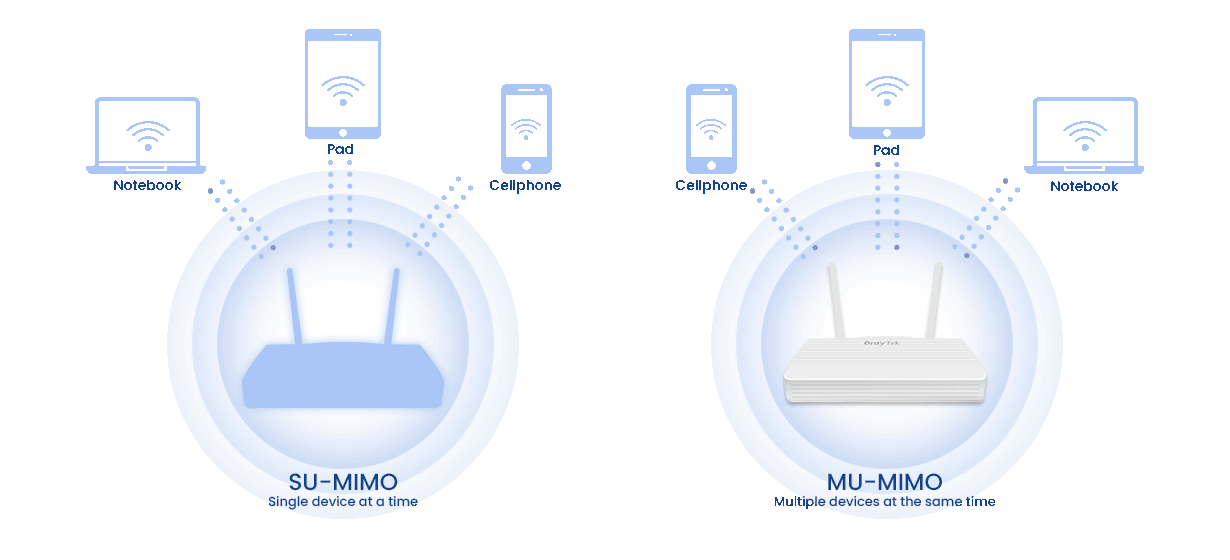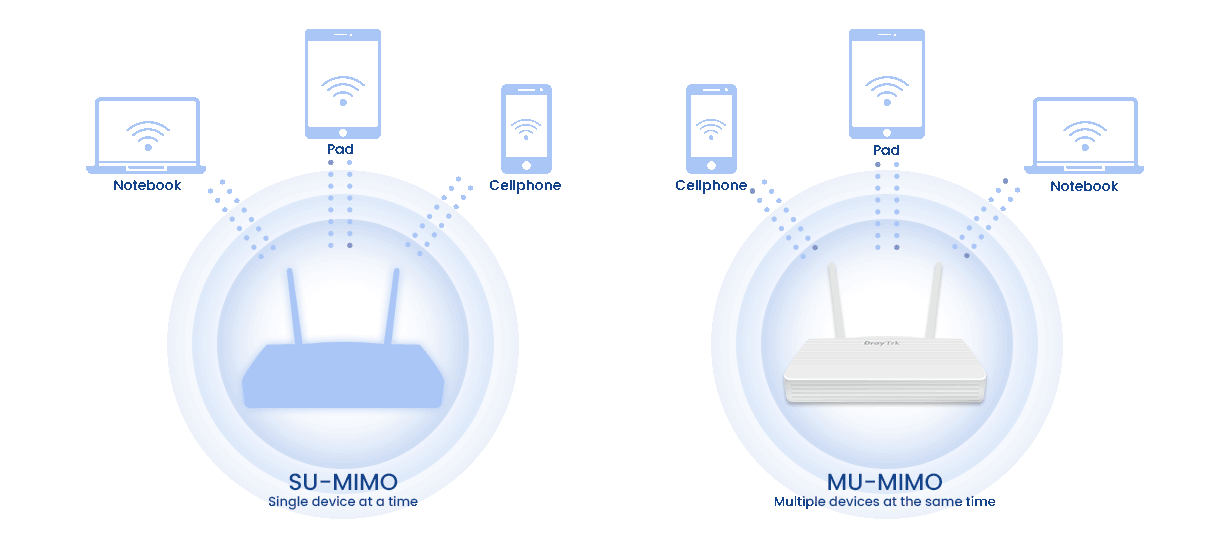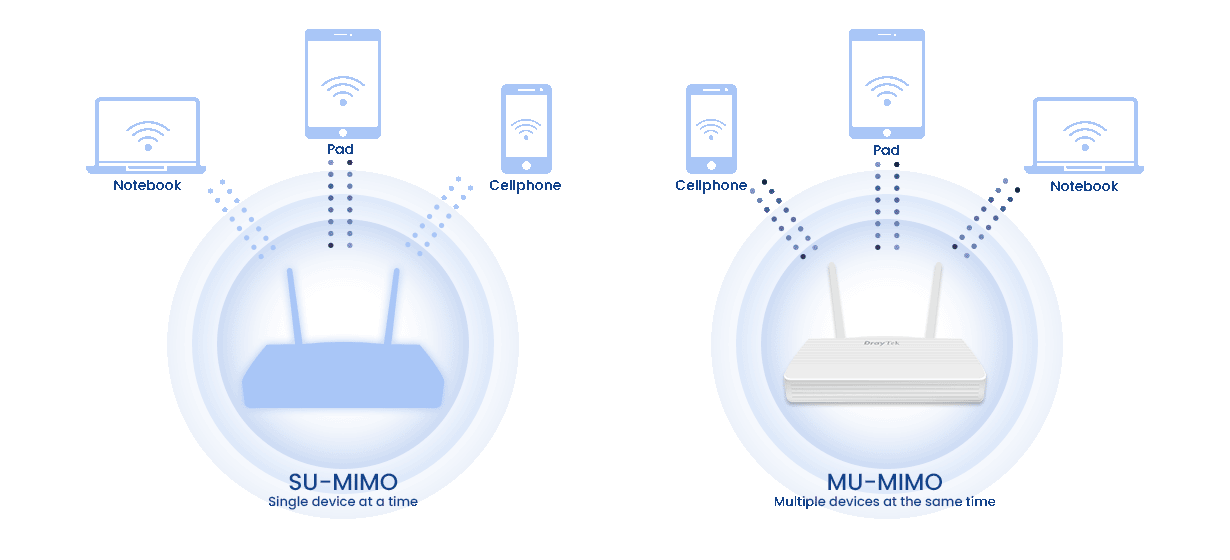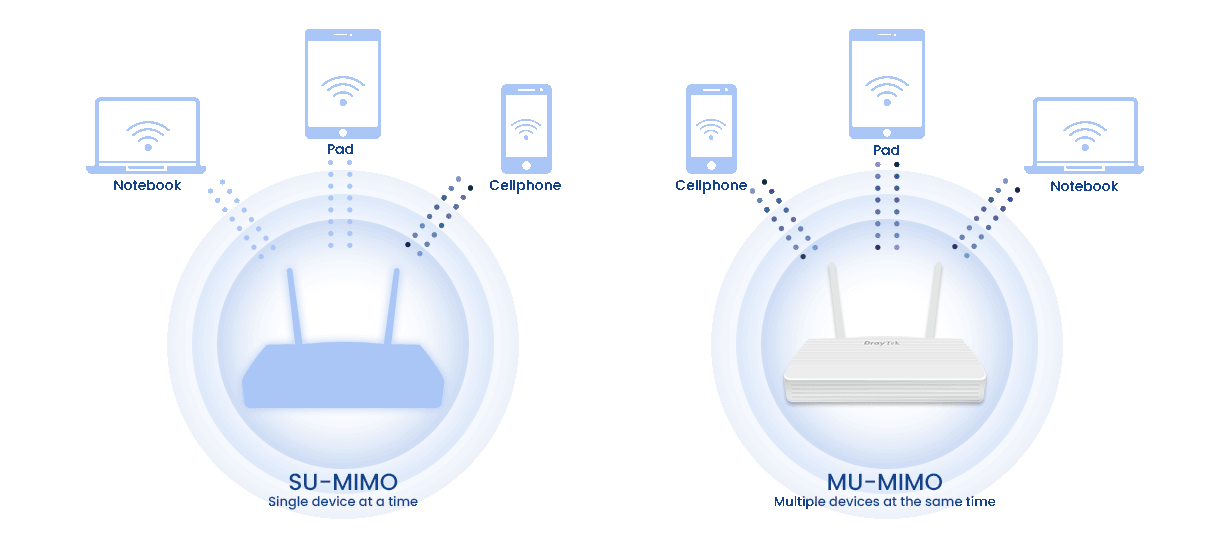
MU-MIMO works like multiple trucks serving users at the same time. It increases capacity and delivers higher speed per user.
BSS Coloring is a technique that improves the coexistence of overlapping BSSs and allows spatial reuse within a single channel. Simply put, BSS Coloring helps reduce the co-channel interference found in legacy Wi-Fi networks.
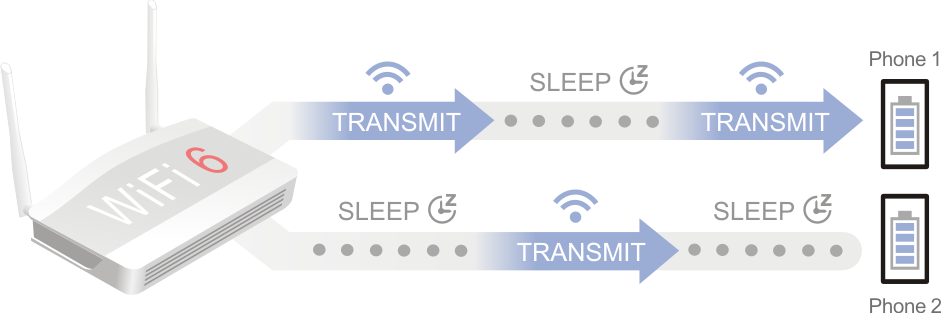
TWT (Target Wake Time) lets end devices spend more time in standby and send and receive data more economically. This reduces energy consumption and improves overall efficiency on the home network. TWT also lets an AP manage activity on the Wi-Fi network to minimize medium contention between stations (STAs) and reduce how long a station in power-save mode needs to stay awake.
WPA3 (Wi-Fi Protected Access 3) strengthens Wi-Fi network security by addressing vulnerabilities in earlier standards such as WPA2 and adding new features to better protect modern wireless communications. Introduced in 2018, WPA3 provides stronger authentication, better encryption, and improved defenses against attacks such as brute-force password guessing and man-in-the-middle exploits.
DrayTek’s Wi-Fi 6 encryption:
- WEP (64 / 128-bit)
- WPA / WPA2 / WPA3 / OWE
The comparison table below shows how clearly WPA3 advances WLAN security design.
| WEP | WPA | WPA2 | WPA3 | |
|---|---|---|---|---|
| Encryption | RC4 | TKIP / RC4 | AES-CCMP | AES-CCMP / AES-GCMP |
| Session Key | 64/128 bit | 128 bit | 128 bit | 128/256 bit |
| Authentication | Open system, shared key | Pre-shared key | Pre-shared key | AES-CCMP / AES-GCMP |
| Level of Security | Very low | Low | Moderate | High |
URL Reputation
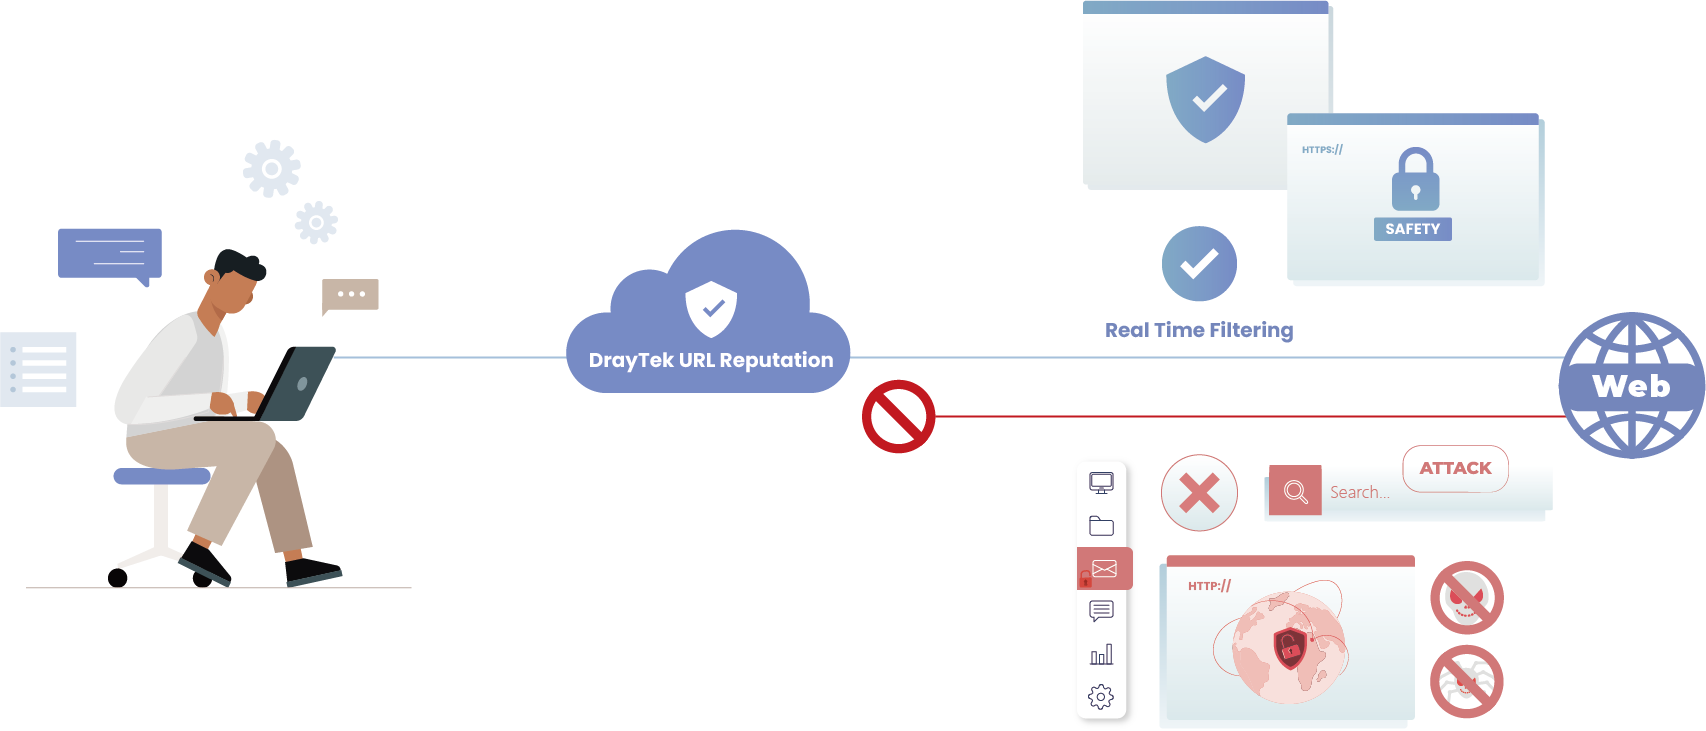
URL Reputation is a cloud-based Threat Intelligence Service that adds an extra layer of security for LAN clients during their online activities.
It offers 82 categories in total, 10 of them security-focused, to provide comprehensive, up-to-date protection for your home or office network.
The categories span network security (including malware, spyware, and adware), parental controls for child protection, business, social networking, and more. Together they help keep the online environment safe, boost employee productivity, and support efficient bandwidth management.
IP Reputation
Every internet communication involves two IP addresses: a source and a destination. Cybercriminals often use known malicious IP addresses to launch attacks with techniques such as:
- Botnets
- TOR nodes and anonymous proxies
- Command-and-control (C2) servers
- Phishing servers
- DDoS attacks
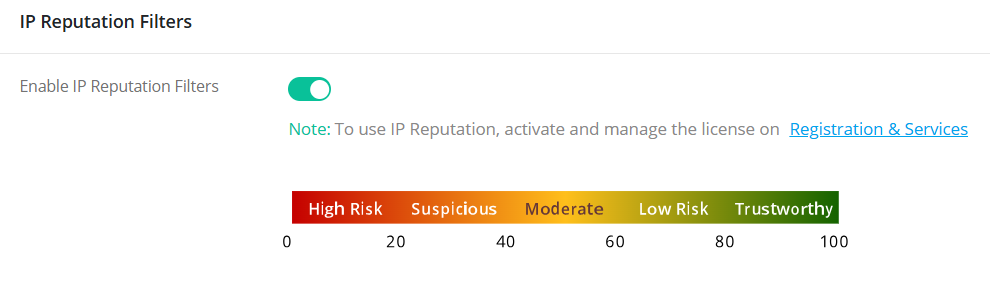
Blocking communication with these harmful IPs is essential, but it takes dynamic, predictive intelligence—something static blocklists can’t provide. The IP Reputation Service solves this by scoring and classifying IP addresses in real time, so it can automatically block:
- High-risk traffic
- Suspicious proxies
- Malware distributors
- IPs linked to recent malicious behavior
The system evaluates each IP against multiple criteria, including infection history, protocol usage, and attack frequency. Each IP receives a reputation score that determines whether it is trusted, monitored, or blocked outright.
Threat Protection Sentry AI-assisted Firewall
Up to 100 LAN Devices • Multi-Layer Defense • Cloud-Enhanced Security
Unified Protection
Router Protection
- Anti-DoS/DDoS, Port Scan Blocker, Brute Force Defense, IP/URL Reputation
Network Protection
- Device fingerprinting, anomaly detection, auto-quarantine of risky devices
IoT / Unmanaged Device Security
- DPI virtual hot patching, exploit prevention, command injection blocking
Web Protection
- Safe Browsing, Category Filtering, Service Filtering, user-assigned policy
Cloud-Driven Intelligence
- Real-time threat analytics
- Updated malicious IP/URL lists
- Centralized reports & event visibility
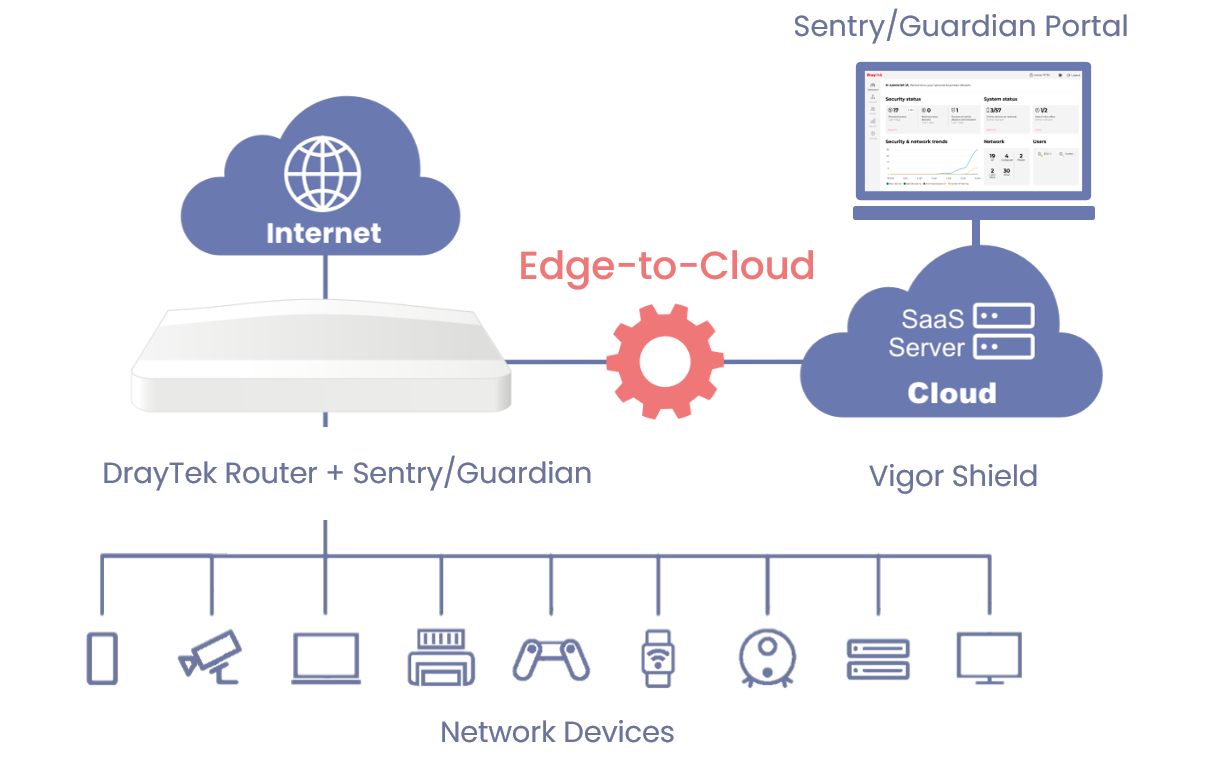
*Note: URL/IP Reputation and Threat Protection cannot be enabled at the same time; each router can run only one of these services.
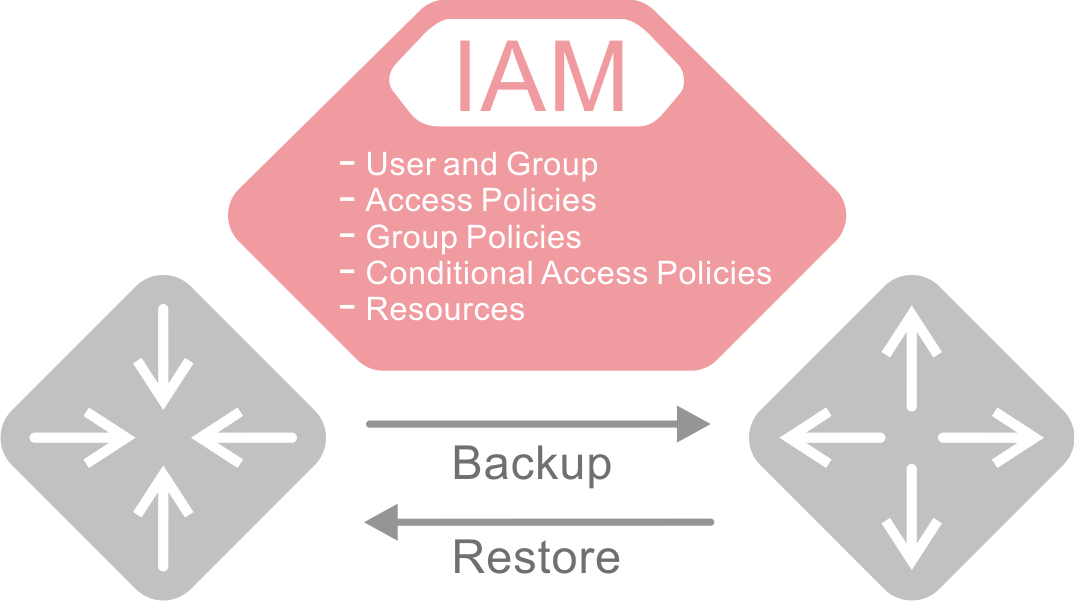
IAM Identity and Access Management
Vigor2136 Series with the new DrayOS 5 is Zero Trust ready!
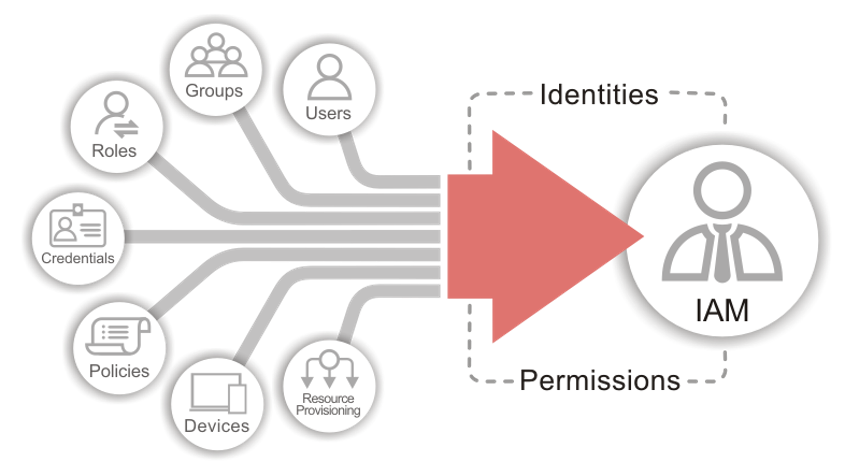
IAM (Identity and Access Management) is a framework of policies and processes that makes sure the right users or groups have appropriate access to critical resources by managing digital identities, authentication, and access control.
It covers the processes for identifying, authenticating, and authorizing users or groups to access systems, applications, and data. By assigning specific roles to users and making sure they have the right level of access to corporate resources and networks, IAM improves both security management and the user experience.
IAM provides a Zero Trust Ready set of security management tools for Vigor routers. It lets you grant and categorize user privileges, create and manage access policies, and define large-scale group policies that combine multiple filtering rules and traffic shaping settings. DrayTek’s IAM plays an important role in your cloud security strategy.
Users & Groups
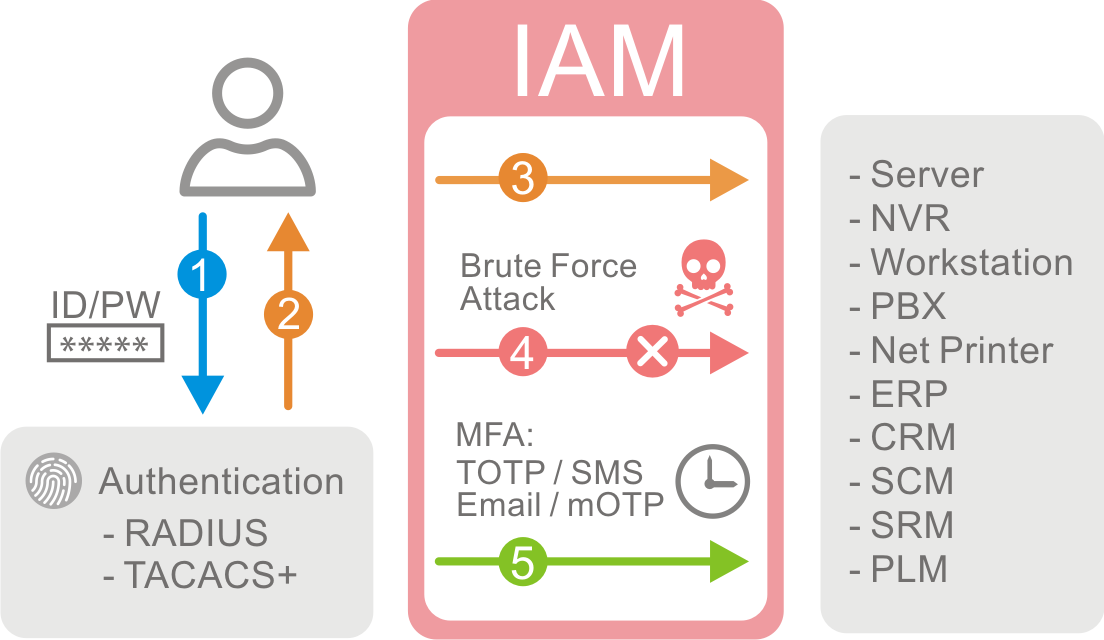
- User account > user groups makes it easy to control and manage accounts in a group level
- Configure external authentication server
- Enable user and MFA protection
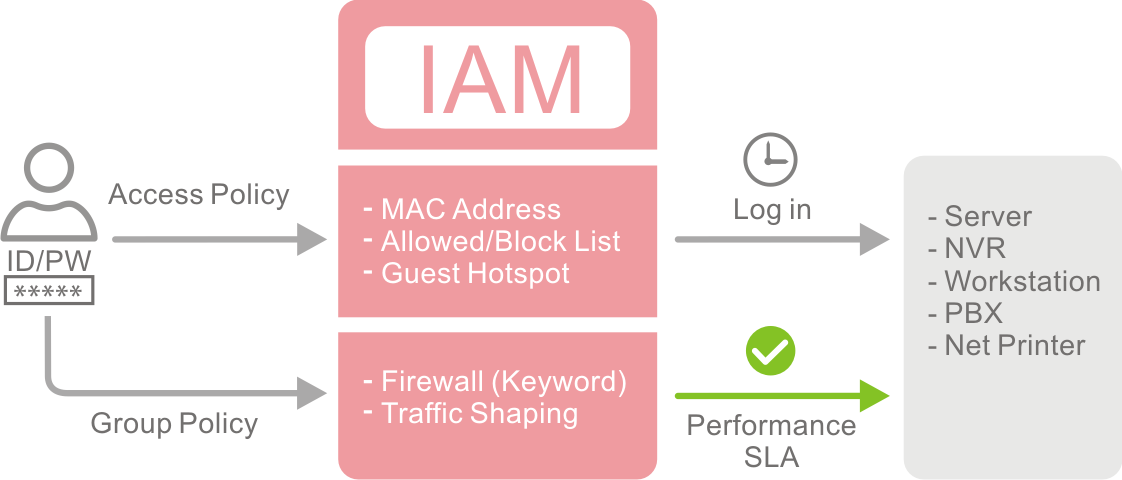
Access Policies
In this tab, system administrators can create access policies for local users. Access policies can be created based on:
- MAC address filter list
- The allowed /blocked user list
- The login sessions lifetime
Combining these access policies creates a robust security framework for your system.
Group Policies
Set up group policies with predefined local resources such as employees, workstations, network printers, and local servers. Customize firewall and traffic shaping policies to strengthen network security and optimize traffic flow.
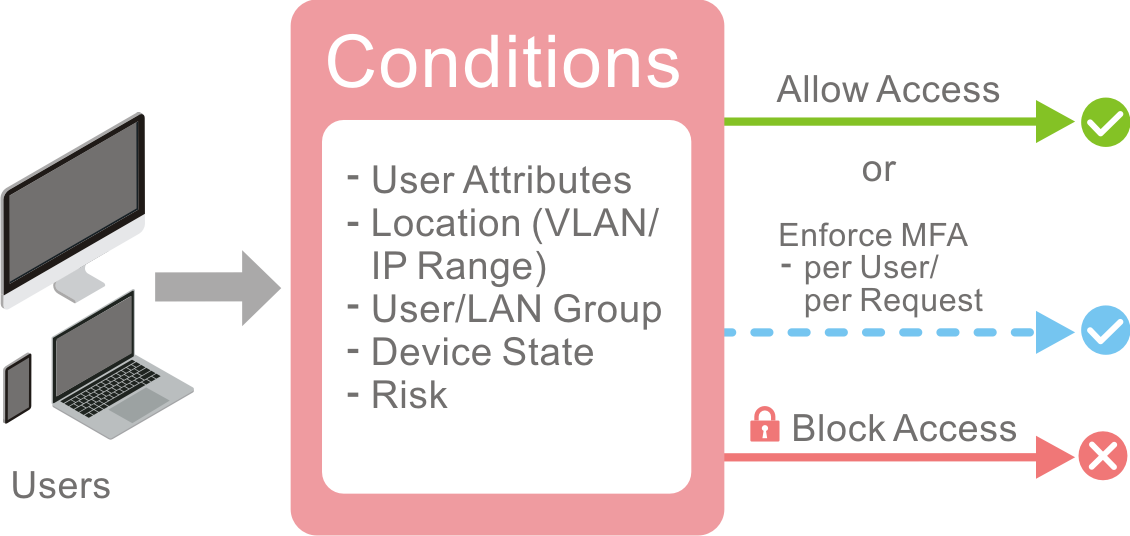
Conditional Access Policy
Conditional access policies can require users to provide multiple forms of authentication before they are granted access to a resource.
- Specify a time period for user to re-authenticate
- Restrict access to specific source IP address or ranges of IP addresses
- Specify VLAN-based access controls in your conditional policies
- Set up time schedules when user are allowed to log-in
Resources
Record the IP and MAC addresses of local resources, such as workstations, network printers, PBX systems, NVR systems, and servers, under the Resources tab.
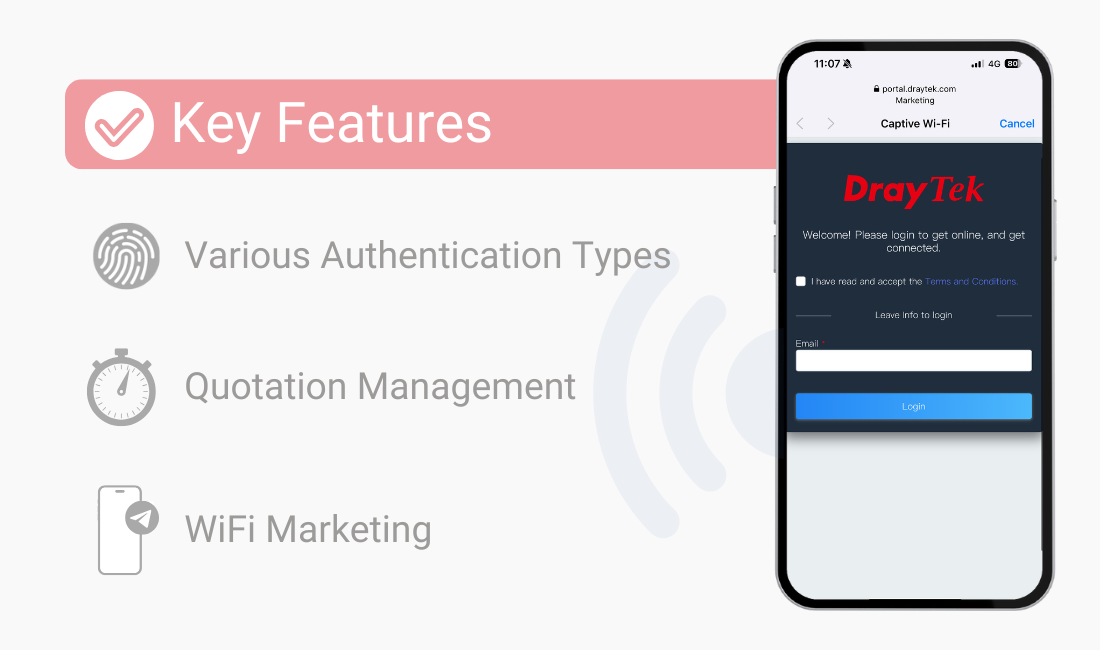
Hotspot Web Portal
DrayTek’s Hotspot Web Portal is a customizable Wi-Fi login page with multiple login options, including username/password, social media, and vouchers. It offers quota management, Wi-Fi marketing for promotions, and branding options. Administrators can control access, set bandwidth limits, and monitor usage.
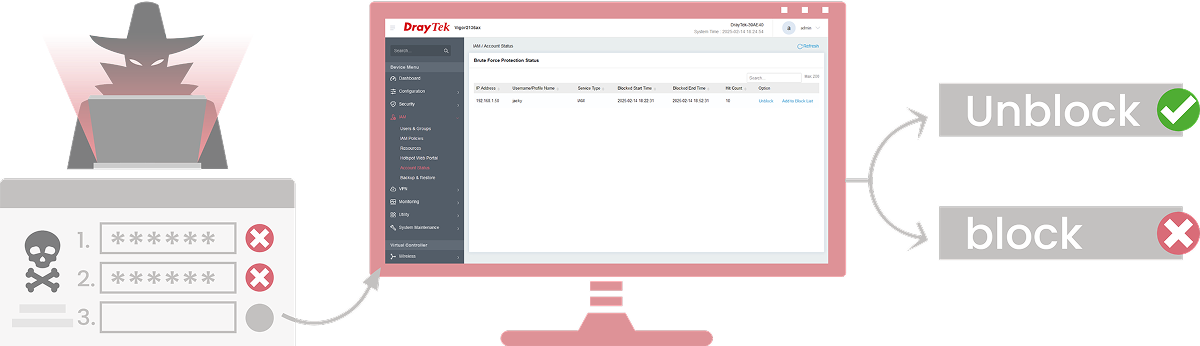
Account Status
The account status feature includes brute-force protection, which logs the attacking IP address, the targeted username or profile, and the type of service under attack.
It also tracks the protection period, recording when blocking starts and ends, along with the total number of hits. You can also unblock access manually if a restriction was applied by mistake.
Backup and Restore
You can back up or restore any of your settings, such as Users and Groups, Access and Group Policies, and more. You can also add password protection to keep the backup files safe before you take action.
Seamless Wi-Fi Roaming
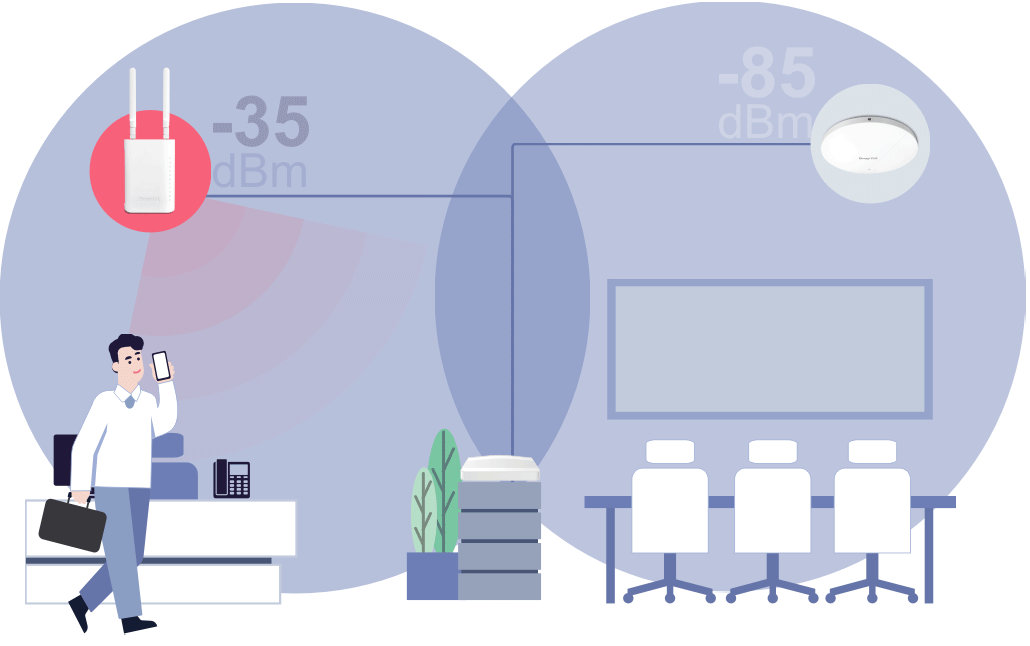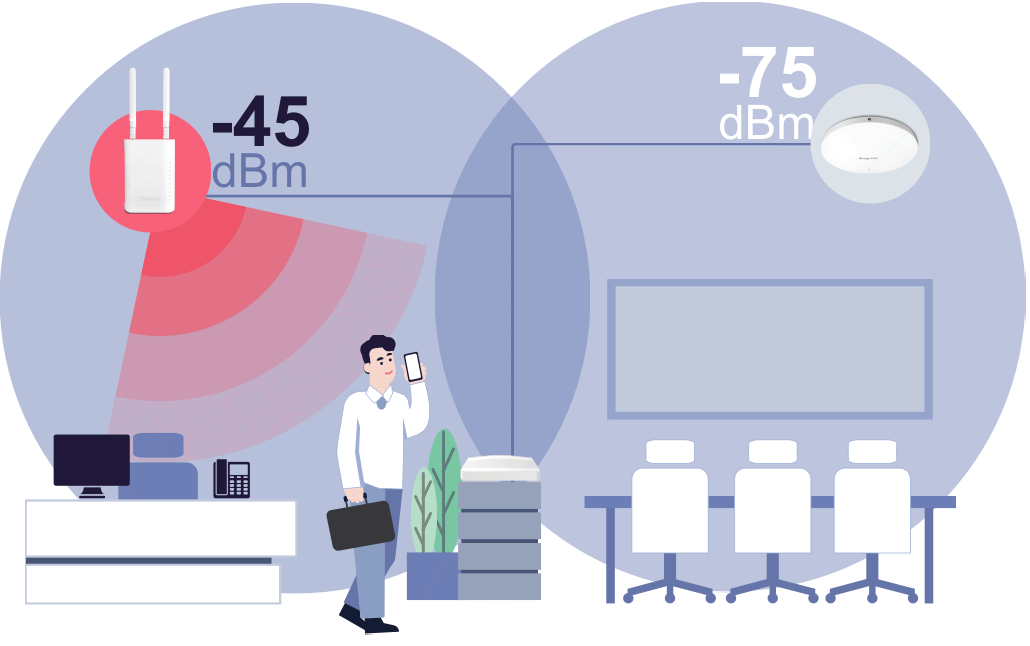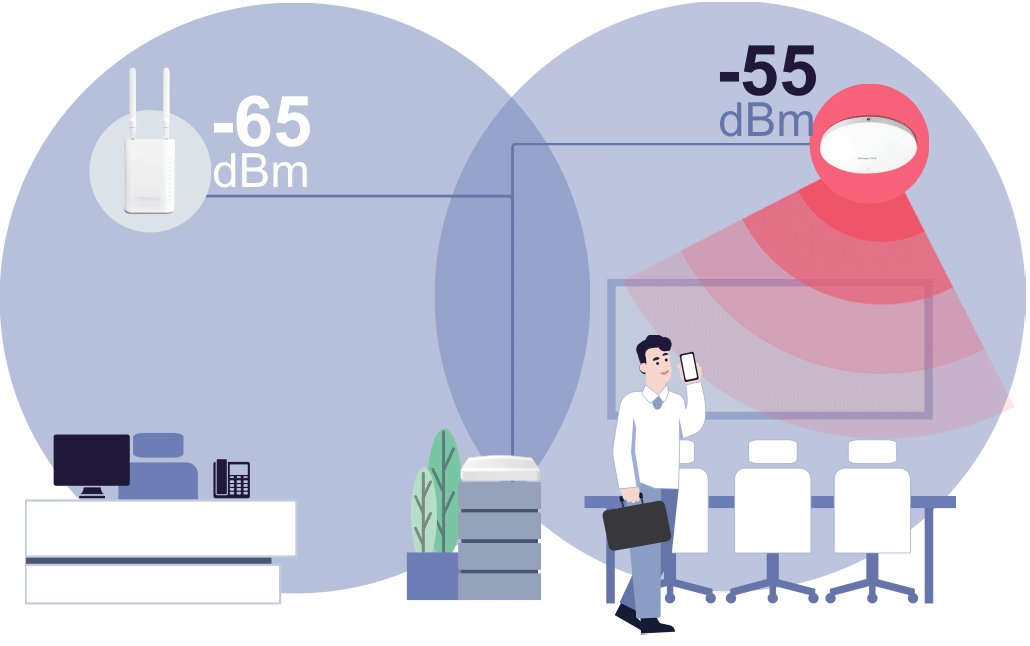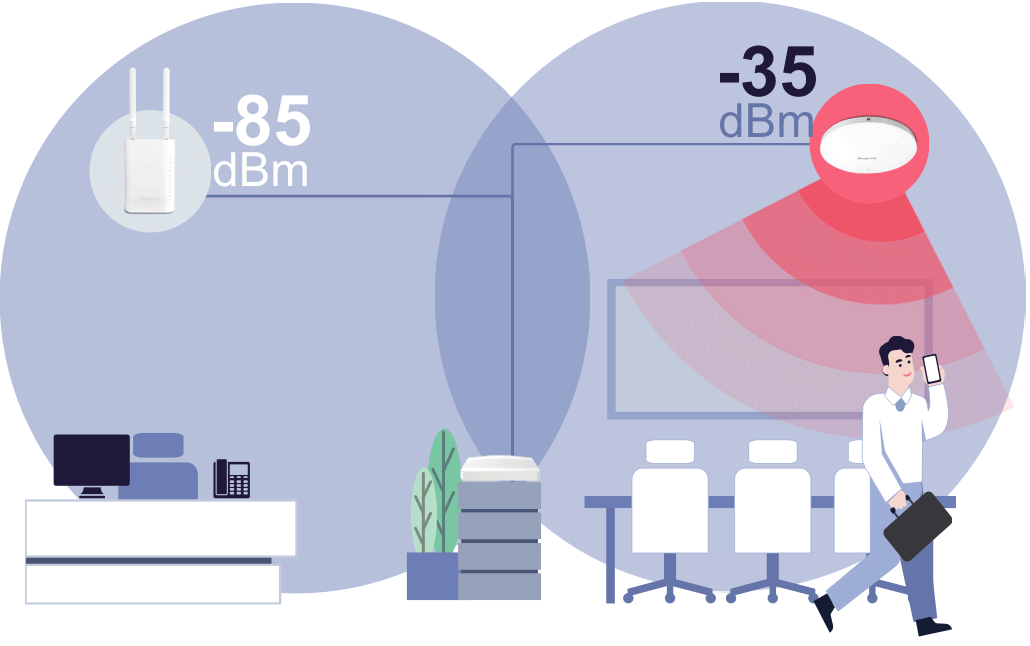
Fast & Smooth Handover
- Switch between access points seamlessly with intelligent roaming support.
- Supports Over-the-DS (via wired backbone) and Over-the-Air handoffs for reliable connectivity during video calls, voice chats, and real-time applications.
Smarter Assisted Roaming
- Signal thresholds and AP steering help devices move to stronger APs and balance network loads.
- Enjoy stable performance across all devices, everywhere.
Always Optimized for Business
- From offices to campuses, seamless roaming ensures uninterrupted mobility.
- Reliable coverage built for the demands of modern workplaces.
Mesh
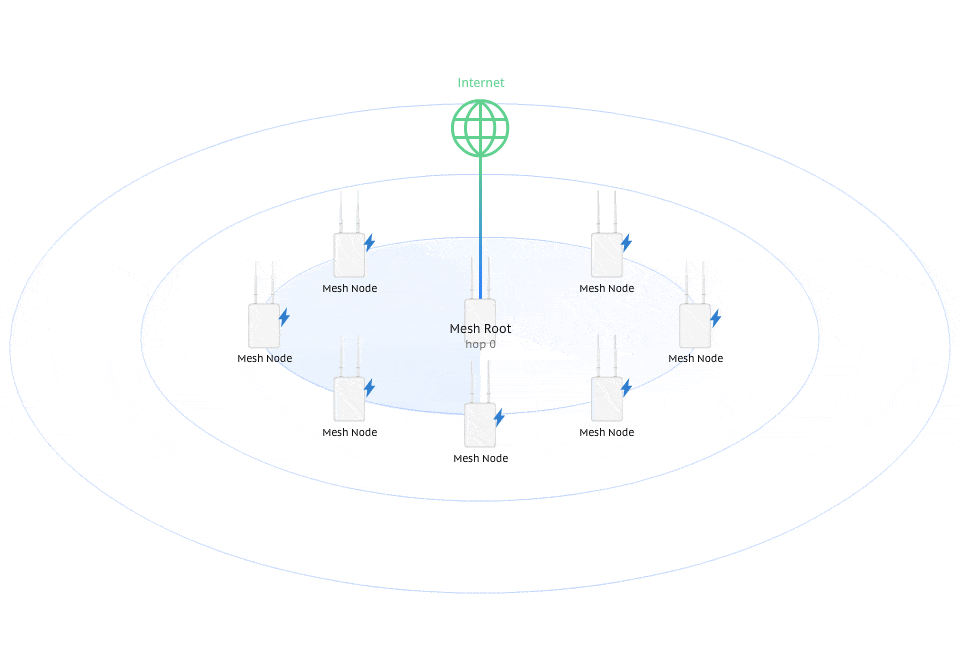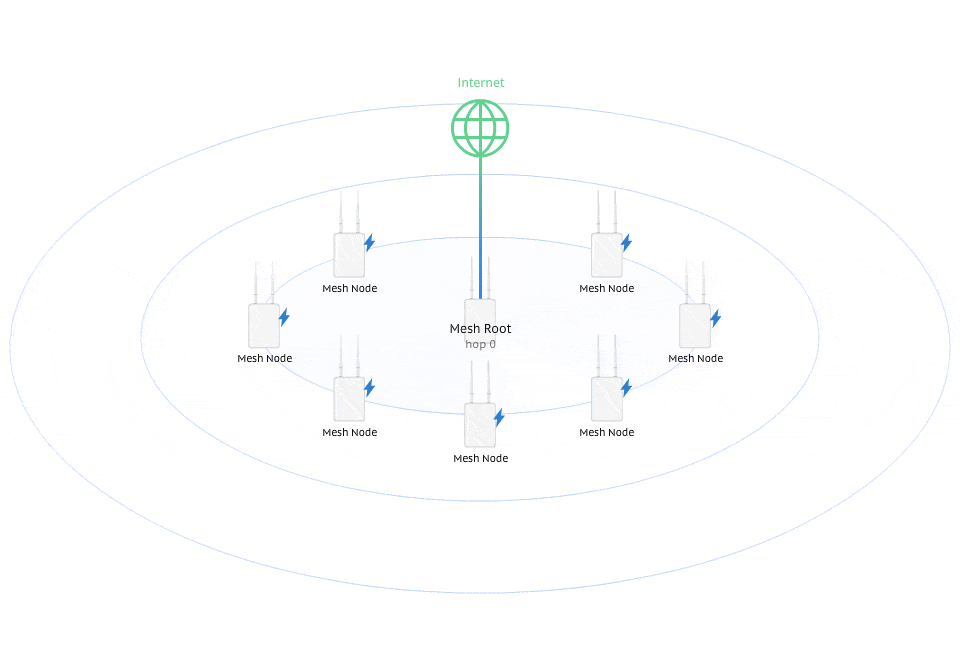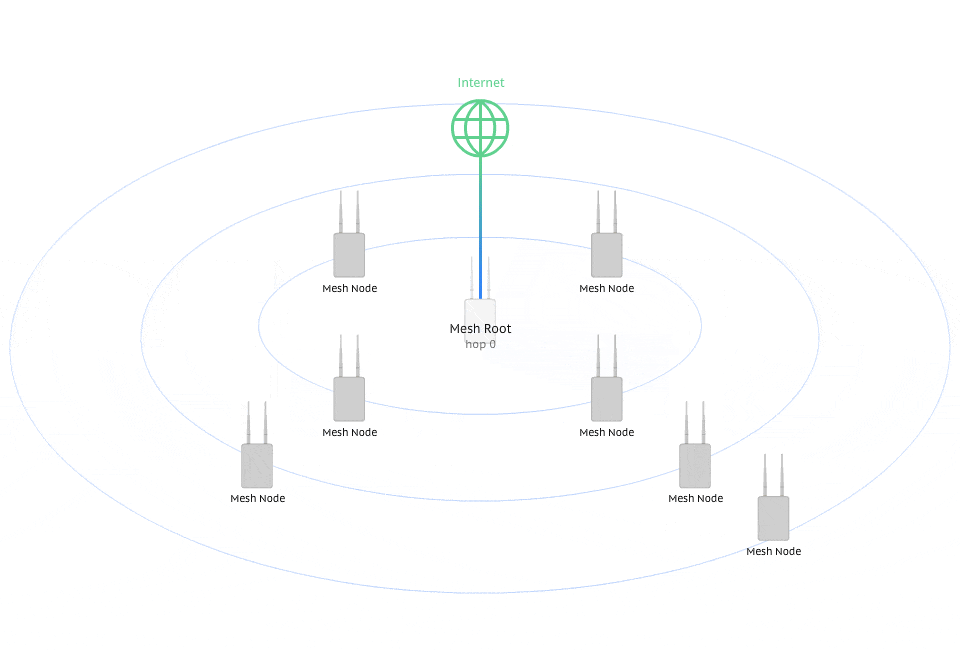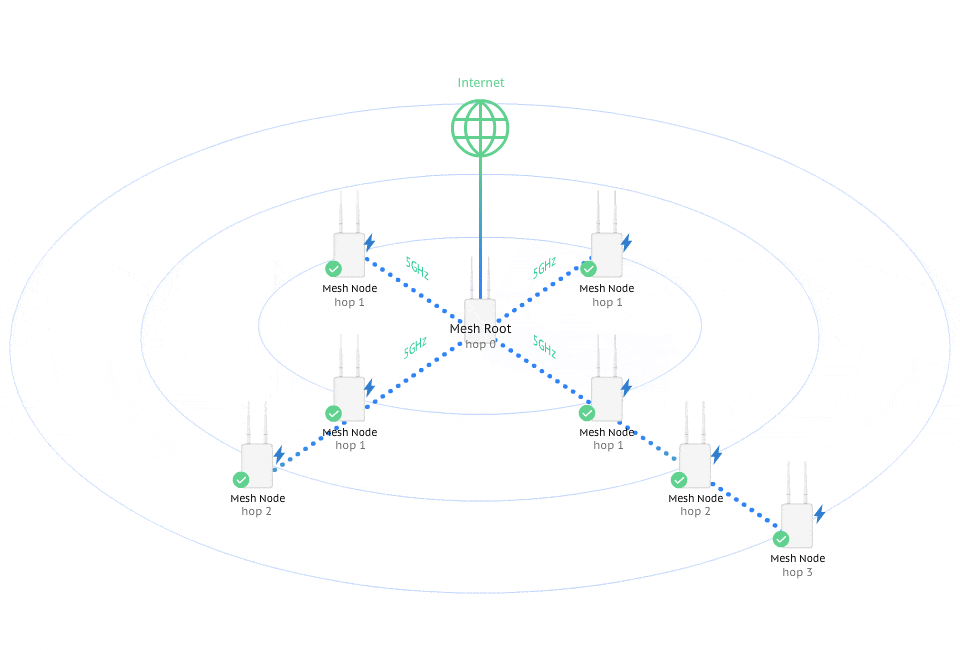
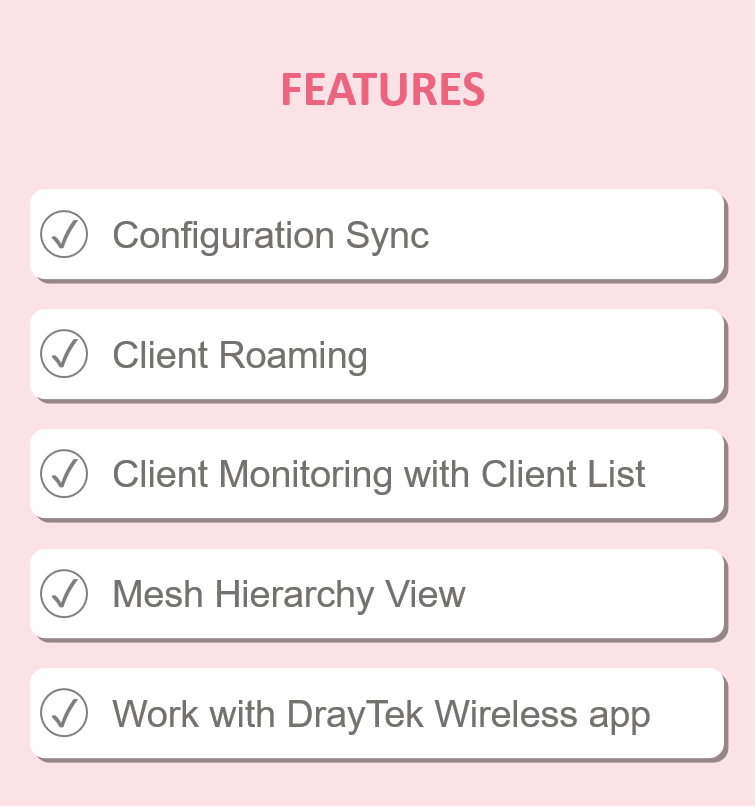
You can connect 7 APs to form a wireless group within the same network, which automatically creates mesh links between the root and node APs based on an optimized algorithm.
Management Solution
Virtual Controller
On-Device Network Management with DrayTek Virtual Controller
DrayTek’s Virtual Controller is a management platform built into supported routers and firewalls. It provides centralized control without depending on the cloud, which reduces data exposure risk and improves network privacy.
Wireless Management
- Mesh Controller: Easily build and manage wireless mesh networks, with auto-routing and self-healing capabilities.
- AP Management (APM): Automatically discover, configure, and monitor connected VigorAPs – ideal for deploying multiple APs with unified settings.
Switch Management
- Central Switch Manager (SWM): Detect and manage supported VigorSwitches, push configurations, monitor status, and apply VLAN or QoS settings – all from one local interface.
Unified Mesh & AP Management
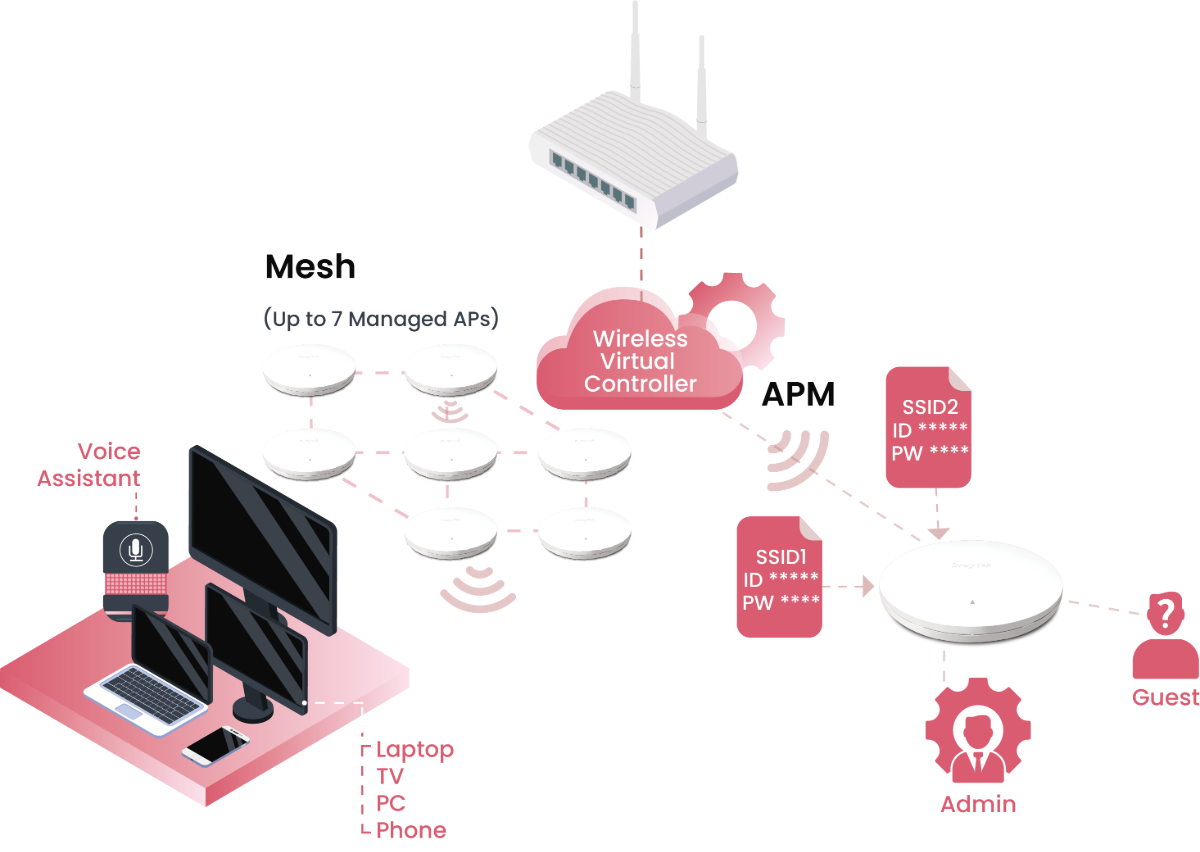
Virtual Controller offers two modes for flexible deployment.
Mesh Mode
Automatically builds a self-healing wireless mesh, with the Vigor2136 Series as the Root AP and up to 7 Node APs, for easy, scalable Wi-Fi coverage.
AP Management Mode
In networks with more than 8 APs, Virtual Controller switches to AP Management mode, so you can centrally control up to 20 APs from the router’s interface.
Seamless Mesh Role Assignment
When devices power on, they discover each other automatically and take on Root or Node AP roles with no manual setup. This automatic role assignment builds a mesh network quickly, with optimized coverage and self-healing capability.
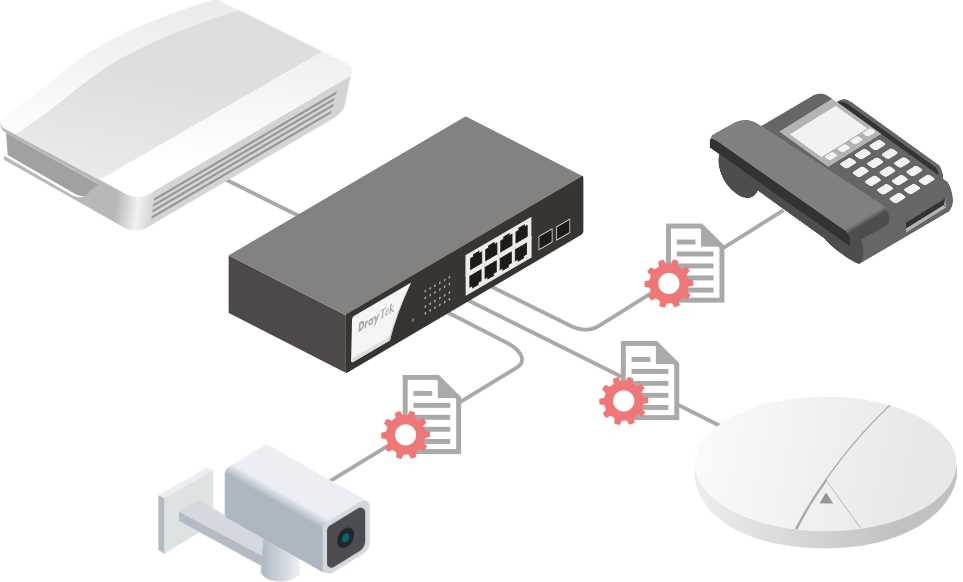
SWM
The Vigor2136 Series can act as the master to manage and monitor up to 5 switches. It also gives you visibility into the PD devices connected behind each switch, such as IP cameras and access points.
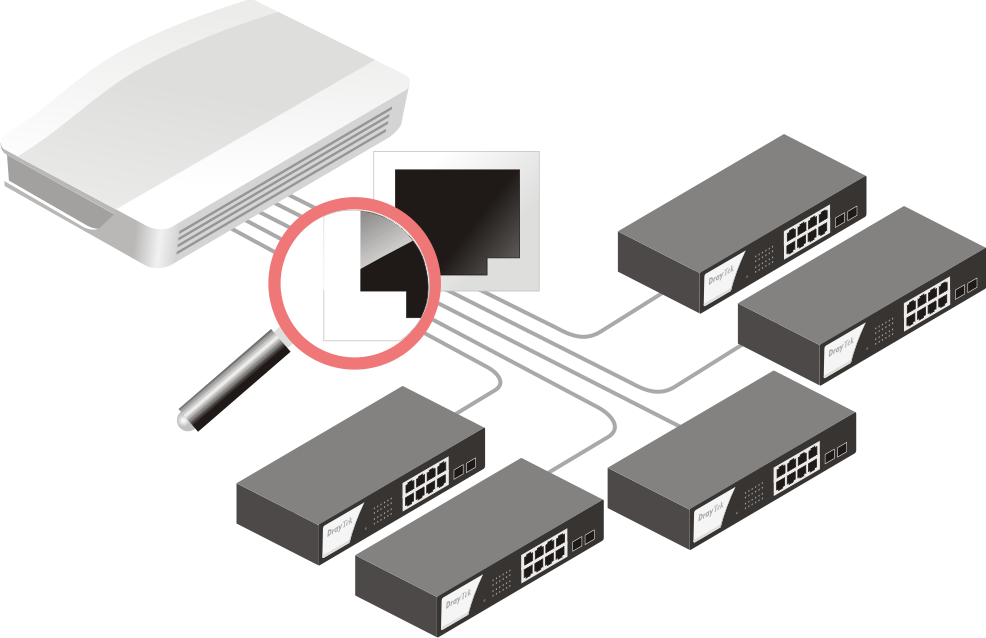
Device Management
Monitor switch status, current firmware version, and uptime for every managed device.
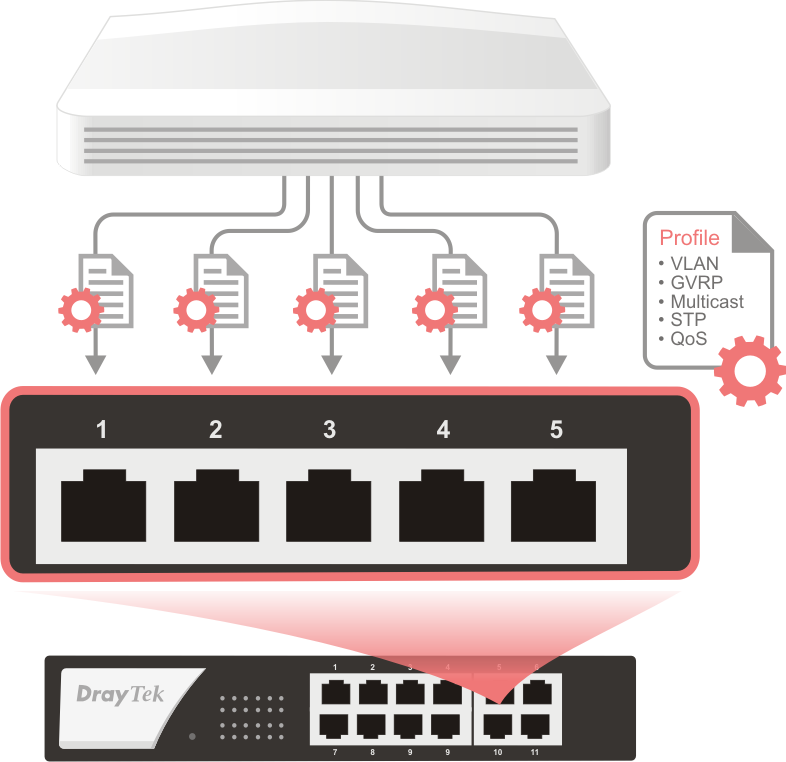
Port Profile
Create multiple port profiles to provision PoE, VLAN, QoS, and other settings on selected switches.
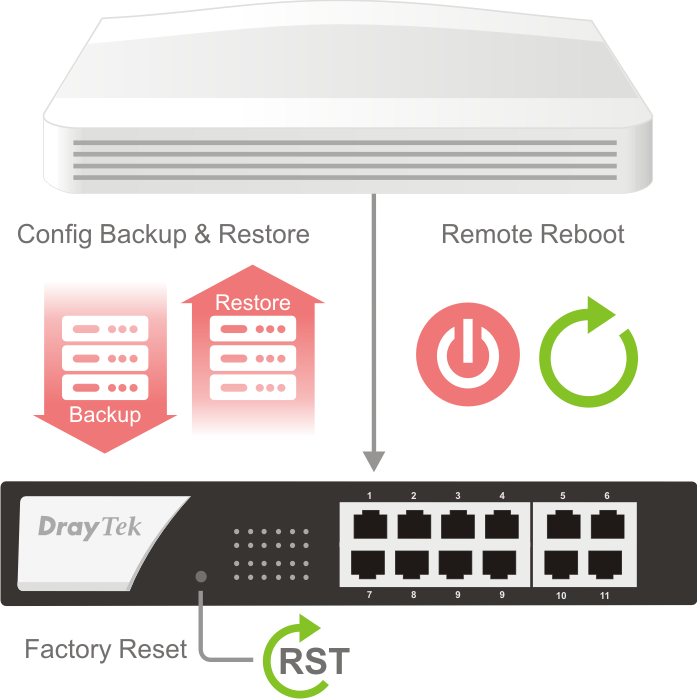
Maintenance
Back up and restore configurations, reboot switches remotely, or reset them to factory defaults.
Software Management
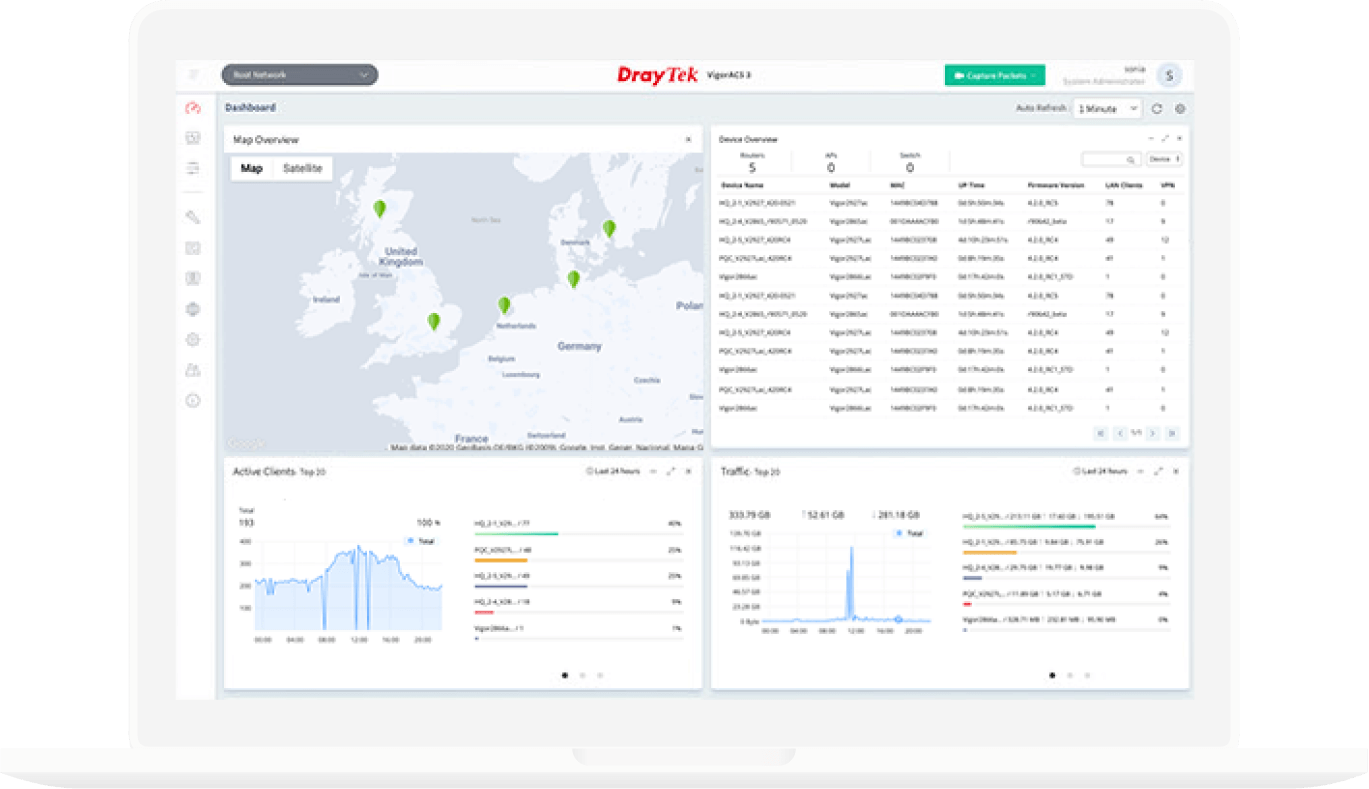
VigorACS 3
- Zero Touch Deployment & Provisioning
- Auto VPN
- Interface Quality & SLA
- VoIP Optimization & Monitoring
- Application Visibility
- Application Based SD-WAN Policy
*Click here to check the support model list. - Customized Hotspot Page with Multilingual
- Hotspot Clients Analytics
- ACS Server Load Balancing / Failover
In the Box
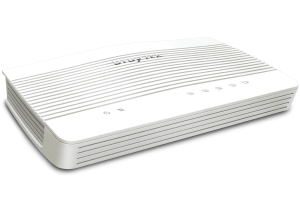 Vigor2136 Series
 Antenna x 2
(ax model) RJ-45 Cable (Ethernet)
 Power Adapter
 Quick Start Guide
Note: Stated throughput figures are maximums from DrayTek internal testing under optimal conditions, with Hardware Acceleration enabled where available. Actual performance may vary depending on network conditions and the applications in use.
Wireless
Unified Mesh & AP Management
Virtual Controller offers two modes for flexible deployment.
Mesh Mode
Automatically builds a self-healing wireless mesh, with the Vigor2136 Series as the Root AP and up to 7 Node APs, for easy, scalable Wi-Fi coverage.
AP Management Mode
In networks with more than 8 APs, Virtual Controller switches to AP Management mode, so you can centrally control up to 20 APs from the router’s interface.
Seamless Mesh Role Assignment
When devices power on, they discover each other automatically and take on Root or Node AP roles with no manual setup. This automatic role assignment builds a mesh network quickly, with optimized coverage and self-healing capability.
Switch
SWM
The Vigor2136 Series can act as the master to manage and monitor up to 5 switches. It also gives you visibility into the PD devices connected behind each switch, such as IP cameras and access points.
Device Management
Monitor switch status, current firmware version, and uptime for every managed device.
Port Profile
Create multiple port profiles to provision PoE, VLAN, QoS, and other settings on selected switches.
Maintenance
Back up and restore configurations, reboot switches remotely, or reset them to factory defaults.
Models
| Model | 2.5G WAN | Wi-Fi WAN (backup) | Wi-Fi 6 | Firewall | VPN |
| Vigor2136 | ✓ | – | – | ✓ | 16 tunnels |
| Vigor2136ax | ✓ | ✓ | ✓ | ✓ | 16 tunnels |
Key Features

2.5GbE
Provides higher performance to Wi-Fi 6 AP and other Ethernet devices.

Bandwidth Management
Prevent one device using all the bandwidth by bandwidth limit policy, session limit policy, and QoS settings.

DrayDDNS
The free DDNS service for you to access the router by a fixed hostname of your choice. Learn more

VPN (Virtual Private Network)
Build a secure and private tunnel from the LAN of Vigor2136 Series to the remote offices and teleworkers over the Internet. Learn more

EasyVPN
Secure VPN in Seconds: No Keys, No Configs, Just Login.

Firewall & Content Filter
Filter web pages by URL keyword or web category to block access to insecure or inappropriate contents.

URL/IP Reputation
Improve network security by classifying URLs and IPs to control web access and protect against online threats. Learn more

IAM
A solution that manages digital identities, authentication, and access control to ensure the right users or groups have appropriate access to critical resources. Learn more

Hotspot Web Portal
Market your business and communicate with the guests while offering hospitality WLAN. Learn more

Wi-Fi 6 (ax model only)
Feature OFDMA and MU-MIMO technology to improve Wi-Fi efficiency and deliver higher wireless speed.


Virtual AP/Switch controller
All-in-one management platform for Vigor2136 Series to maintain and monitor the VigorAPs and VigorSwitches.

Threat Protection
Detect and mitigate cyber threats with cloud-assisted threat intelligence, helping protect users, devices, and networks from malicious activities. Learn more
Specs
Specifications
Model | Vigor2136 | Vigor2136ax |
Performance | ||
| NAT Session | 50K | 50K |
| Max. NAT (Mbps) | 2300 | 2300 |
WAN | ||
| Ethernet (2.5 GbE) | 2 | 2 |
| Ethernet – Switchable * When this field is filled, the port count above includes both switchable and fixed ports. | ✓ (LAN/WAN) | ✓ (LAN/WAN) |
| Cellular (via USB) | 2 | 2 |
| Wireless WAN (2.4GHz + 5GHz) | ✓ | |
Internet Connection | ||
| IPv4 | PPPoE DHCP Static IP | PPPoE DHCP Static IP |
| IPv6 | PPP DHCPv6 Static IPv6 TSPC 6rd 6in4 Static Tunnel | PPP DHCPv6 Static IPv6 TSPC 6rd 6in4 Static Tunnel |
| 802.1p/q Multi-VLAN Tagging | ✓ | ✓ |
| Failover | ✓ | ✓ |
| Connection Detection | ARP, Ping | ARP, Ping |
| WAN Data Budget | ✓ | ✓ |
| Dynamic DNS | ✓ | ✓ |
| DrayDDNS | ✓ | ✓ |
LAN | ||
| Fixed LAN (RJ-45, GbE) | 3 | 3 |
| LAN Subnet | 4 | 4 |
| VLAN | 802.1q Tag-based VLAN | 802.1q Tag-based VLAN |
| Max. Number of VLAN | 8 | 8 |
| DHCP Server | Multiple IP Subnet Custom DHCP Options Bind-IP-to-MAC | Multiple IP Subnet Custom DHCP Options Bind-IP-to-MAC |
| Wired 802.1x Authentication | ✓ | ✓ |
| Port Mirroring | ✓ | ✓ |
| Local DNS Server | ✓ | ✓ |
| Conditional DNS Forwarding | ✓ | ✓ |
| Hotspot Web Portal (Profile No.) | 2 | 2 |
| Hotspot Authentication | Click-Through Social Login SMS PIN RADIUS External Portal Server | Click-Through Social Login SMS PIN RADIUS External Portal Server |
WLAN | ||
| 2.4GHz WLAN | 802.11ax 2×2 MIMO | |
| 5GHz WLAN | 802.11ax 3×3 MU-MIMO | |
| WiFi Antenna (External) | 2 | |
| WiFi Antenna (Internal) | 1 | |
| 2.4GHz Antenna Gain (dBi) | 2.6 | |
| 5GHz Antenna Gain (dBi) | 2.7 | |
| 2.4GHz Max. Link Rate (Mbps) | 574 | |
| 5GHz Max. Link Rate (Mbps) | 2402 | |
| Max. Number of SSIDs (per band) | 8 (4) | |
| Security Mode | OWE WEP WPA WPA2/WPA WPA2 WPA3/WPA2 WPA3 | |
| Authentication | Pre-Shared Key, 802.1X | |
| Wi-Fi 6 | ✓ | |
| OFDMA | ✓ | |
| Roaming | Assisted Roaming | |
| WPS | WPS Button, PIN Code | |
| WDS | Repeater | |
| Access Control | Access List Client Isolation Hide SSID WLAN Scheduling | |
| AirTime Fairness | ✓ | |
| Band Steering | ✓ | |
| WMM | ✓ | |
| Mesh (5GHz Only) | Root | |
Other Ports | ||
| USB | 2 | 2 |
| USB Type | 2.0 | 2.0 |
| USB Application | User Management FTP File Sharing Device Status Printer Server Temperature Sensor USB WAN | User Management FTP File Sharing Device Status Printer Server Temperature Sensor USB WAN |
| SMB File Sharing (Requires external storage) | ✓ | ✓ |
Networking | ||
| Routing | IPv4 Static Route IPv6 Static Route Policy Route Inter-VLAN Route RIP v1/v2 BGP OSPF(V2/V3) | IPv4 Static Route IPv6 Static Route Policy Route Inter-VLAN Route RIP v1/v2 BGP OSPF(V2/V3) |
| Policy-based Routing | Protocol IP Address Port | Protocol IP Address Port |
| DNS Security (DNSSEC) | ✓ | ✓ |
| IGMP | IGMP v2/v3 IGMP Proxy IGMP Snooping & Fast Leave | IGMP v2/v3 IGMP Proxy IGMP Snooping & Fast Leave |
| Local RADIUS server | ✓ | ✓ |
Bandwidth Management | ||
| Traffic Shaping Policy | ✓ | ✓ |
| IP-based Bandwidth Limit | ✓ | ✓ |
| IP-based Session Limit | ✓ | ✓ |
| QoS (Quality of Service) | IP Address Port Application | IP Address Port Application |
| APP QoS | ✓ | ✓ |
| Default Policy | ✓ | ✓ |
| VoIP Prioritization | ✓ | ✓ |
NAT | ||
| Port Forwarding | ✓ | ✓ |
| DMZ Host | ✓ | ✓ |
| Port Trigger | ✓ | ✓ |
| ALG (Application Layer Gateway) | SIP, RTSP, FTP, H.323 | SIP, RTSP, FTP, H.323 |
| UPnP | ✓ | ✓ |
Management | ||
| Local Service | HTTP HTTPS Telnet SSH v2 FTP TR-069 | HTTP HTTPS Telnet SSH v2 FTP TR-069 |
| Config Backup/Restore | ✓ | ✓ |
| Firmware Upgrade | WUI, TFTP, TR-069 | WUI, TFTP, TR-069 |
| Role-based Privilege | ✓ | ✓ |
| Access Control | Access List, Brute Force Protection | Access List, Brute Force Protection |
| Notification Alert | SMS, E-mail | SMS, E-mail |
| SNMP | v1, v2c, v3 | v1, v2c, v3 |
| Syslog | ✓ | ✓ |
| Virtual AP Controller (Device up to) | 20 | 20 |
| Mesh (Number of manageable APs) | 7 | |
| Virtual Switch Controller | 5 | 5 |
| VigorACS Management (Since f/w) | V5.3.0 | V5.3.0 |
Security | ||
| URL/IP Reputation | ✓ | ✓ |
| Threat Protection | ✓ | ✓ |
| Firewall Filter | IP, Content, Traffic | IP, Content, Traffic |
| Port Knocking | ✓ | ✓ |
| Defense Setup | ARP Spoofing, IP Spoofing | ARP Spoofing, IP Spoofing |
| MAC Filtering Profile | ✓ | ✓ |
| IPv6 Address Security | ✓ | ✓ |
IAM | ||
| Users & Groups | ✓ | ✓ |
| Access Policies | ✓ | ✓ |
| Group Policies | ✓ | ✓ |
| Conditional Access Policy | ✓ | ✓ |
| Resources | ✓ | ✓ |
| Account Status | ✓ | ✓ |
| Backup and Restore | ✓ | ✓ |
VPN | ||
| Site-to-Site VPN | ✓ | ✓ |
| Teleworker VPN | ✓ | ✓ |
| EasyVPN | ✓ | ✓ |
| Protocols | IPsec L2TP over IPsec IKEv1/IKEv2 IKEv2-EAP IPsec-XAuth OpenVPN WireGuard | IPsec L2TP over IPsec IKEv1/IKEv2 IKEv2-EAP IPsec-XAuth OpenVPN WireGuard |
| Max. VPN Tunnels | 16 | 16 |
| IPsec VPN Throughput (AES 256 bits) (single-directional) (Mbps) | 390 | 390 |
| WireGuard VPN Throughput (single-directional) (Mbps) | 50 | 50 |
| User Authentication | Local RADIUS TACACS+ mOTP TOTP | Local RADIUS TACACS+ mOTP TOTP |
| IKE Authentication | Pre-Shared Key, X.509 | Pre-Shared Key, X.509 |
| IPsec Authentication | SHA-1, SHA-256 | SHA-1, SHA-256 |
| Encryption | DES, 3DES, AES | DES, 3DES, AES |
| Single-Armed VPN | ✓ | ✓ |
| NAT-Traversal (NAT-T) | ✓ | ✓ |
| VPN Matcher | ✓ | ✓ |
| VPN Connection Status | ✓ | ✓ |
| Backup & Restore | ✓ | ✓ |
Monitoring | ||
| Clients List | ✓ | ✓ |
| Log Center | ✓ | ✓ |
| Wireless Information | ✓ | |
| WAN | ✓ | ✓ |
| ARP Table | ✓ | ✓ |
| Route Table | ✓ | ✓ |
| DHCP Table | ✓ | ✓ |
| IPv6 TSPC Status | ✓ | ✓ |
| IPv6 Neighbor Table | ✓ | ✓ |
| LLDP Neighbors | ✓ | ✓ |
| DNS Cache Table | ✓ | ✓ |
| Remote DSL Status | ✓ | ✓ |
| SFP Information | ✓ | ✓ |
| PPPoE Pass-Through | ✓ | ✓ |
| Session Table | ✓ | ✓ |
| Running Service | ✓ | ✓ |
Physical | ||
| Power Input | DC 12V @ 0.9A | DC 12V @ 1.5A |
| Max. Power Consumption (watts) | 10 | 18 |
| Dimension (mm) | 207 x 131 x 42 | 207 x 131 x 42 |
| Operating Temperature | 0 to 45°C | 0 to 45°C |
| Storage Temperature | -25 to 70°C | -25 to 70°C |
| Operating Humidity (non-condensing) | 10 to 90% | 10 to 90% |
Note:
- * : Future Support
- The stated throughput performance figures are the maximum derived from DrayTek internal testing, conducted under optimal conditions, with Hardware Acceleration enabled where available. The actual performance may vary based on network conditions and activated applications.
Accessories
Resources
Firmware
Vigor2136 Firmware Version 5.4.4.2
Vigor2136 Firmware Version 5.4.4.2 Release Note